
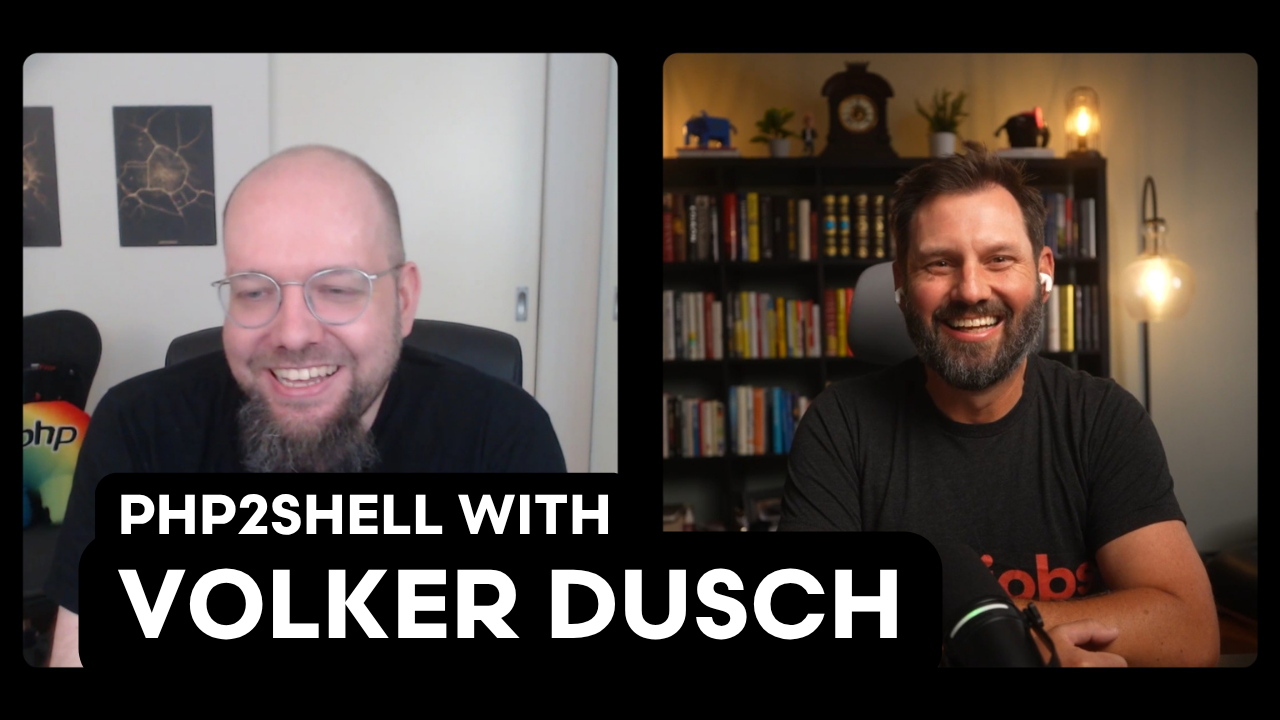
I sat down with Volker Dusch for the Laravel Creator Sequence to speak about this week’s important PHP safety releases. Volker works at Tideways and is at the moment the AI Safety Engineer in Residence on the PHP Basis’s Ecosystem Safety Group, and he labored with the PHP safety staff on these fixes.
We coated how the 2 vulnerabilities had been reported, why a PHP repair takes longer to succeed in your server than a browser replace, the embargo that acquired damaged, and what the PHP Basis is taking away from it.
How the Vulnerabilities Have been Discovered
The PHP Basis acquired PHP into OpenAI’s Patch the Planet program, and the safety agency Calif began an audit of PHP as a part of it. Not lengthy after, Calif emailed Volker asking to fulfill urgently. That they had a minimal exploit working in a Docker container, and as soon as the PHP safety staff noticed it, everybody agreed it was actual. OpenAI and Wiz reported extra assault vectors with the identical root trigger.
Why the Repair Took Coordination
Volker defined that the PHP challenge ships supply code, not the PHP you put in. The repair has to undergo Debian, Ubuntu, Crimson Hat, the official Docker Hub photographs, and the pictures constructed on high of these. Due to the severity, the staff additionally helped coordinate backports for variations PHP not helps, and OpenAI and Wiz reached out to the massive cloud hosts the staff did not have direct contacts with.
The staff additionally labored with net utility firewall distributors reminiscent of Cloudflare so they may ship guidelines earlier than launch day, which protects websites that do not patch immediately.
The Damaged Embargo
Distributors acquired the patch early so their customers may replace the second the vulnerabilities went public. Chainguard broke that embargo and printed patched photographs greater than six hours earlier than the coordinated launch. Volker identified that anybody can now flip a patch, or perhaps a binary, into an exploit a lot quicker than earlier than:
It’s a tough promote to say you are engaged on safety for those who go away the general public uncovered.
Pretend Proofs of Idea
We additionally talked concerning the exploit screenshots going round social media. Volker stated a number of of those he checked solely labored in opposition to a Docker container that had been specifically modified, and did nothing in opposition to the default picture from Docker Hub.
The oldsters that we work with know use AI as a device to make themselves higher and to not simply offload your considering to the machine.
The Session Add Progress Advisory
PHP printed a follow-up advisory at present that recommends setting session.upload_progress.enabled=0 till the following common bugfix launch. That setting was already one of many mitigations in Wednesday’s advisory, so for those who utilized it then, you need not do the rest. Volker stated the situations for this one are very specific and it is minor compared.
Who Did the Work
Volker made some extent of crediting Ilija, Arnaud, and Jakub, who spent their days and nights in PHP’s C code whereas he dealt with communication. As a result of the bug sample may present up in lots of locations, lacking a single one would have meant one other launch:
Now we have to repair each place the place this occurs. Each place means if we miss one it is an issue.
These builders are paid full time by the PHP Basis, which is why the staff may drop every little thing else for this. If your organization builds on PHP, Volker asks you to contemplate sponsoring the Basis:
In the event you make a ton of cash off of constructing apps on high of PHP, giving again only a tiny fraction of that could be very helpful.
Give the video a watch, and an enormous because of Volker for making time for this in such a busy week!

