
If the NTFS permissions behind a share are locked down, why does each auditor nonetheless circle the road that claims Everybody, Full Management?
And in the event that they aren’t locked down, which share has no one checked because the file server was constructed, and would one Get-SmbShare | Get-SmbShareAccess pipeline catch it?
Stipulations
To reply each questions by yourself file server, you want:
| Requirement | Particulars |
|---|---|
| Account | Can question shares on the file server, equivalent to an area administrator |
| PowerShell | Runs on that server. Microsoft paperwork the SmbShare cmdlets for Home windows Server 2016 by 2025, and PowerShell hundreds the module on first use. |
Why Everybody Full Management Will get Flagged
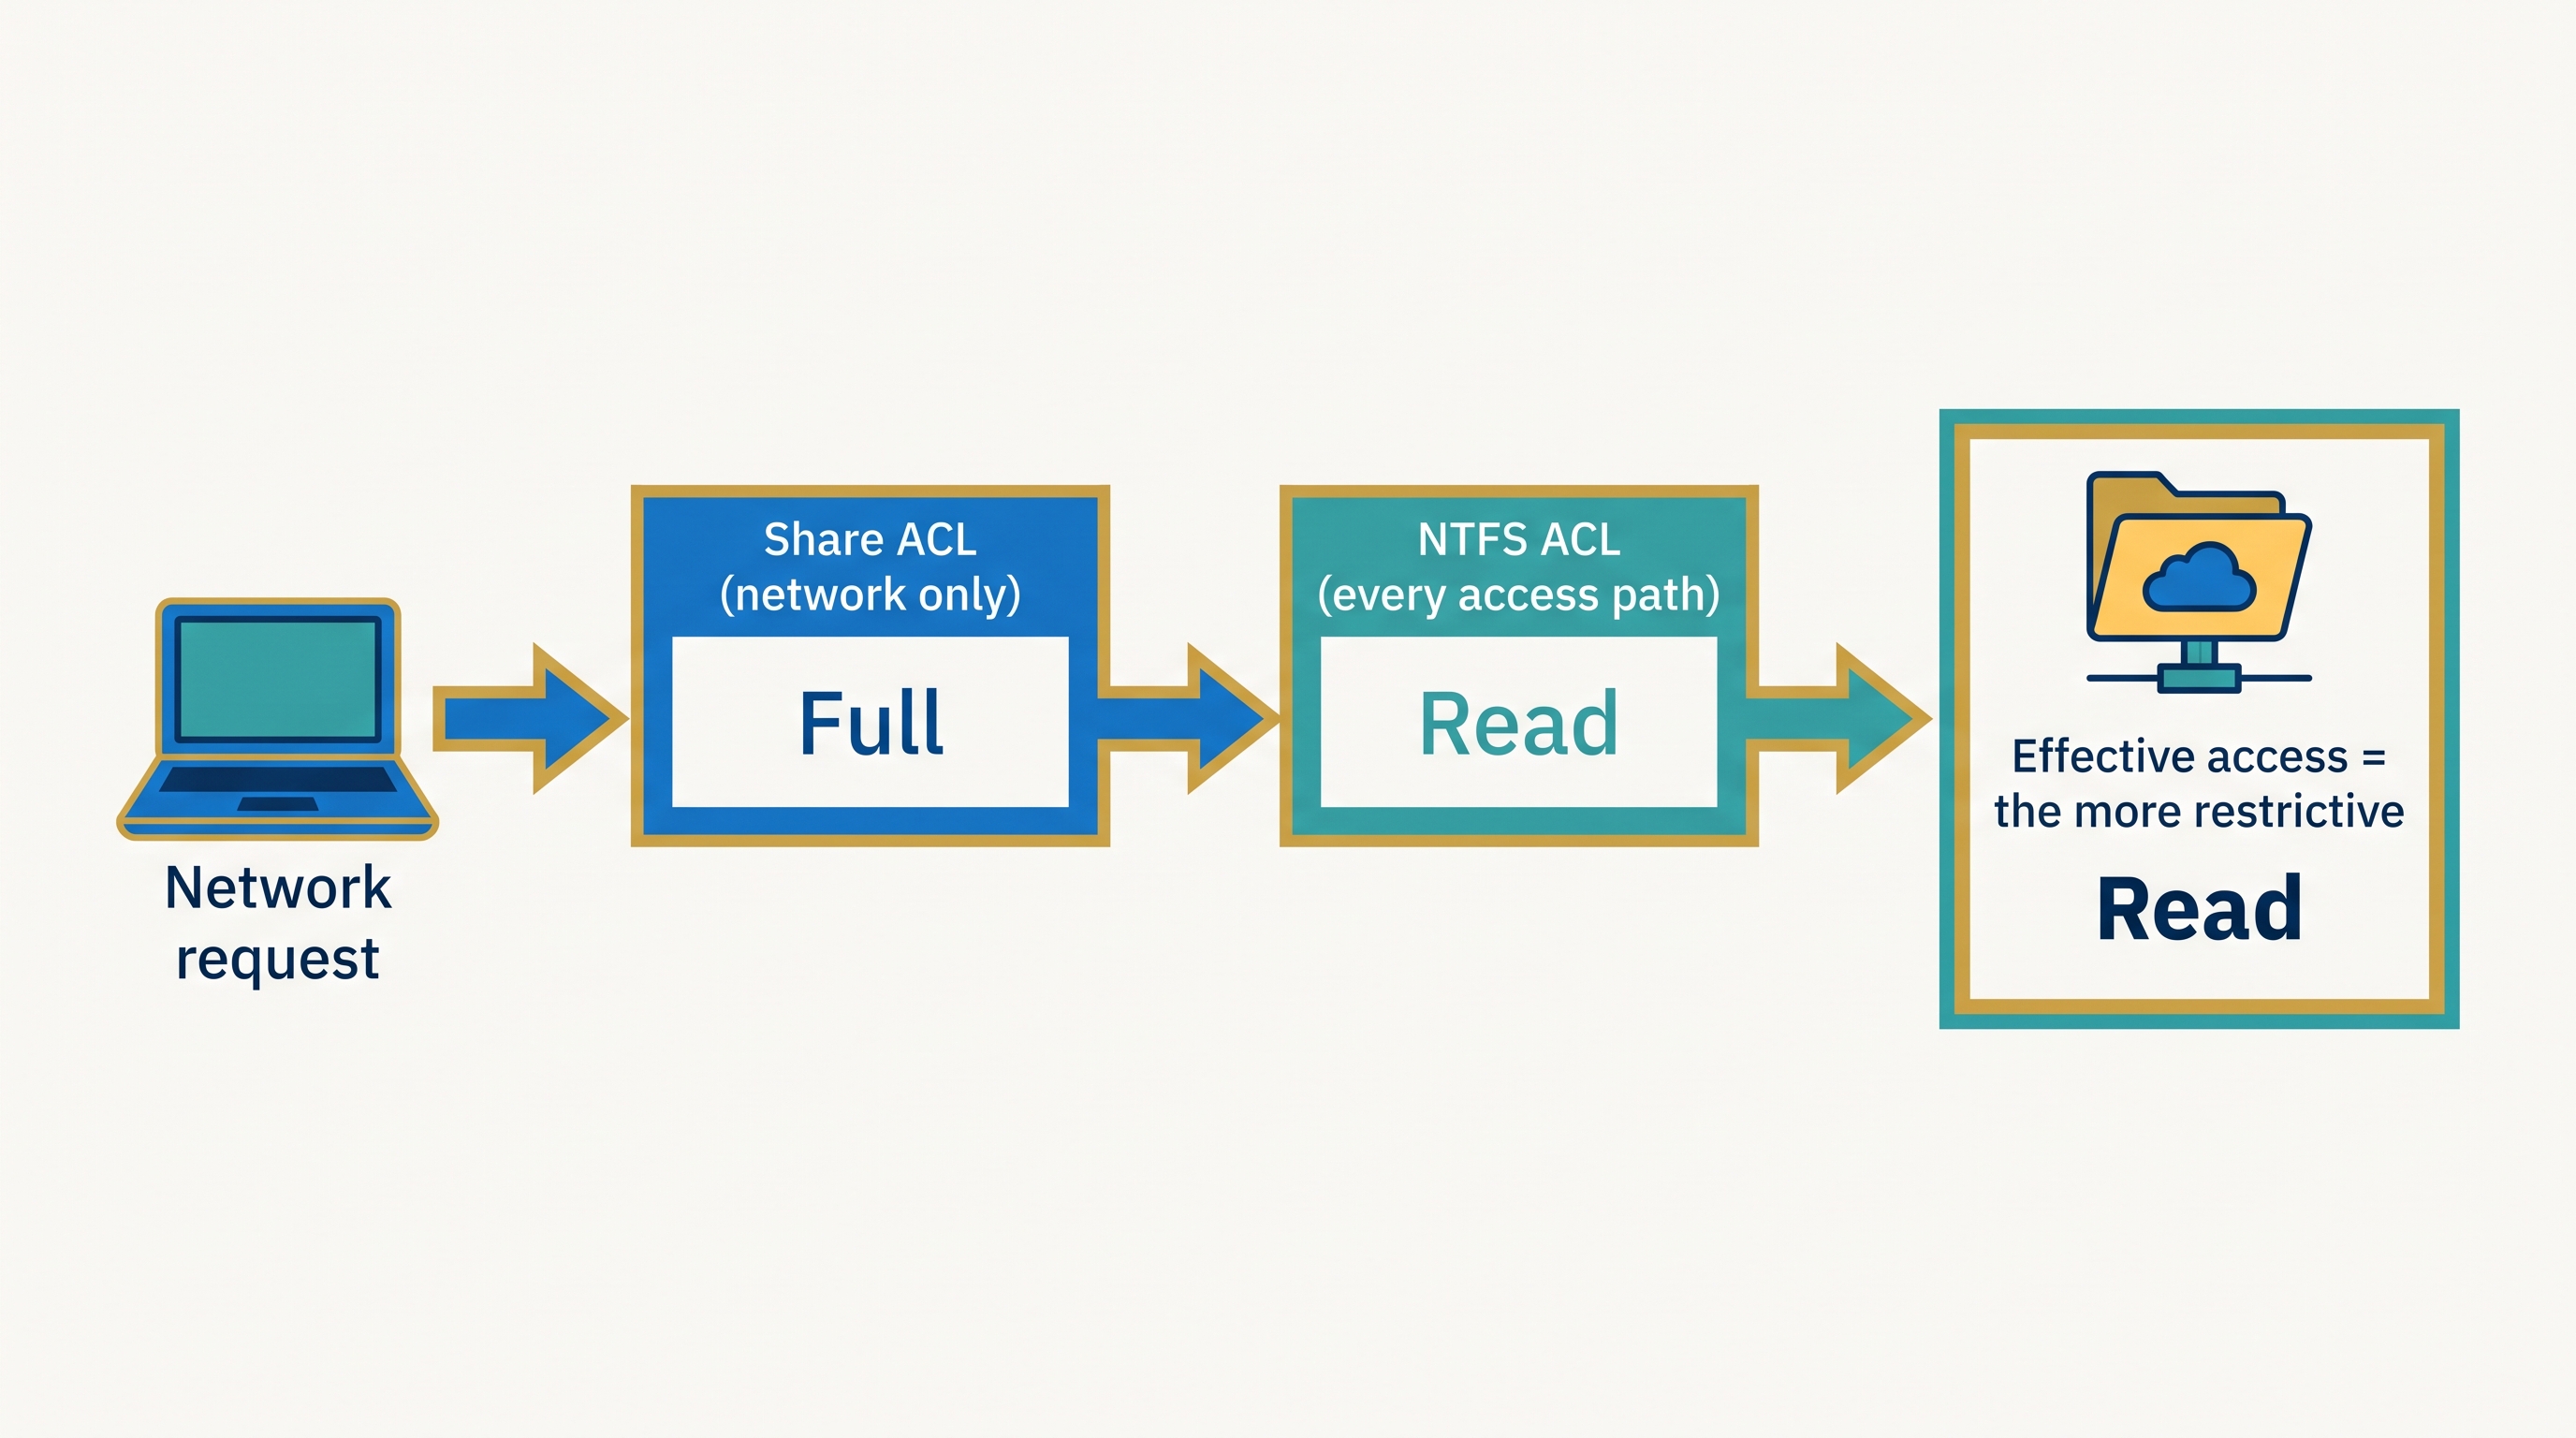
Each community request to a share passes two permission checks. The share ACL (the entry record saved on the share) applies solely to community connections. The NTFS ACL on the folder applies to each entry path.
Microsoft’s information to managing permissions for shared folders says: “NTFS permissions and share permissions are unbiased within the sense that neither modifications the opposite, and essentially the most restrictive of the 2 shall be utilized to the shared useful resource.”
The diagram under reveals one request passing each checks.
Microsoft’s shared-folder information additionally recommends the grant you’re searching: “If you wish to handle folder and quantity entry by utilizing NTFS permissions completely, set share permissions to Full Management for Everybody.”
Even a deliberate Everybody grant deserves scrutiny, as a result of the NTFS ACL turns into the one safety; one unintentional loosening exposes the folder.
Everybody additionally covers lower than the title suggests. Microsoft’s particular id teams reference states: “Starting in Home windows Server 2003, the Everybody group comprises solely Authenticated Customers and Visitor.” Each signed-in account nonetheless qualifies, so every share’s NTFS ACL decides who will get in.
Flag Dangerous Grants with Get-SmbShareAccess
Run this on the file server. It lists user-created shares, reads every entry record, and retains any enable entry that matches both take a look at:
Get-SmbShare -Particular $false |
    Get-SmbShareAccess |
    The place-Object {
        $_.AccessControlType -eq 'Enable' -and
        ($_.AccountName -eq 'Everybody' -or $_.AccessRight -eq 'Full')
    } |
    Choose-Object Title, AccountName, AccessRight
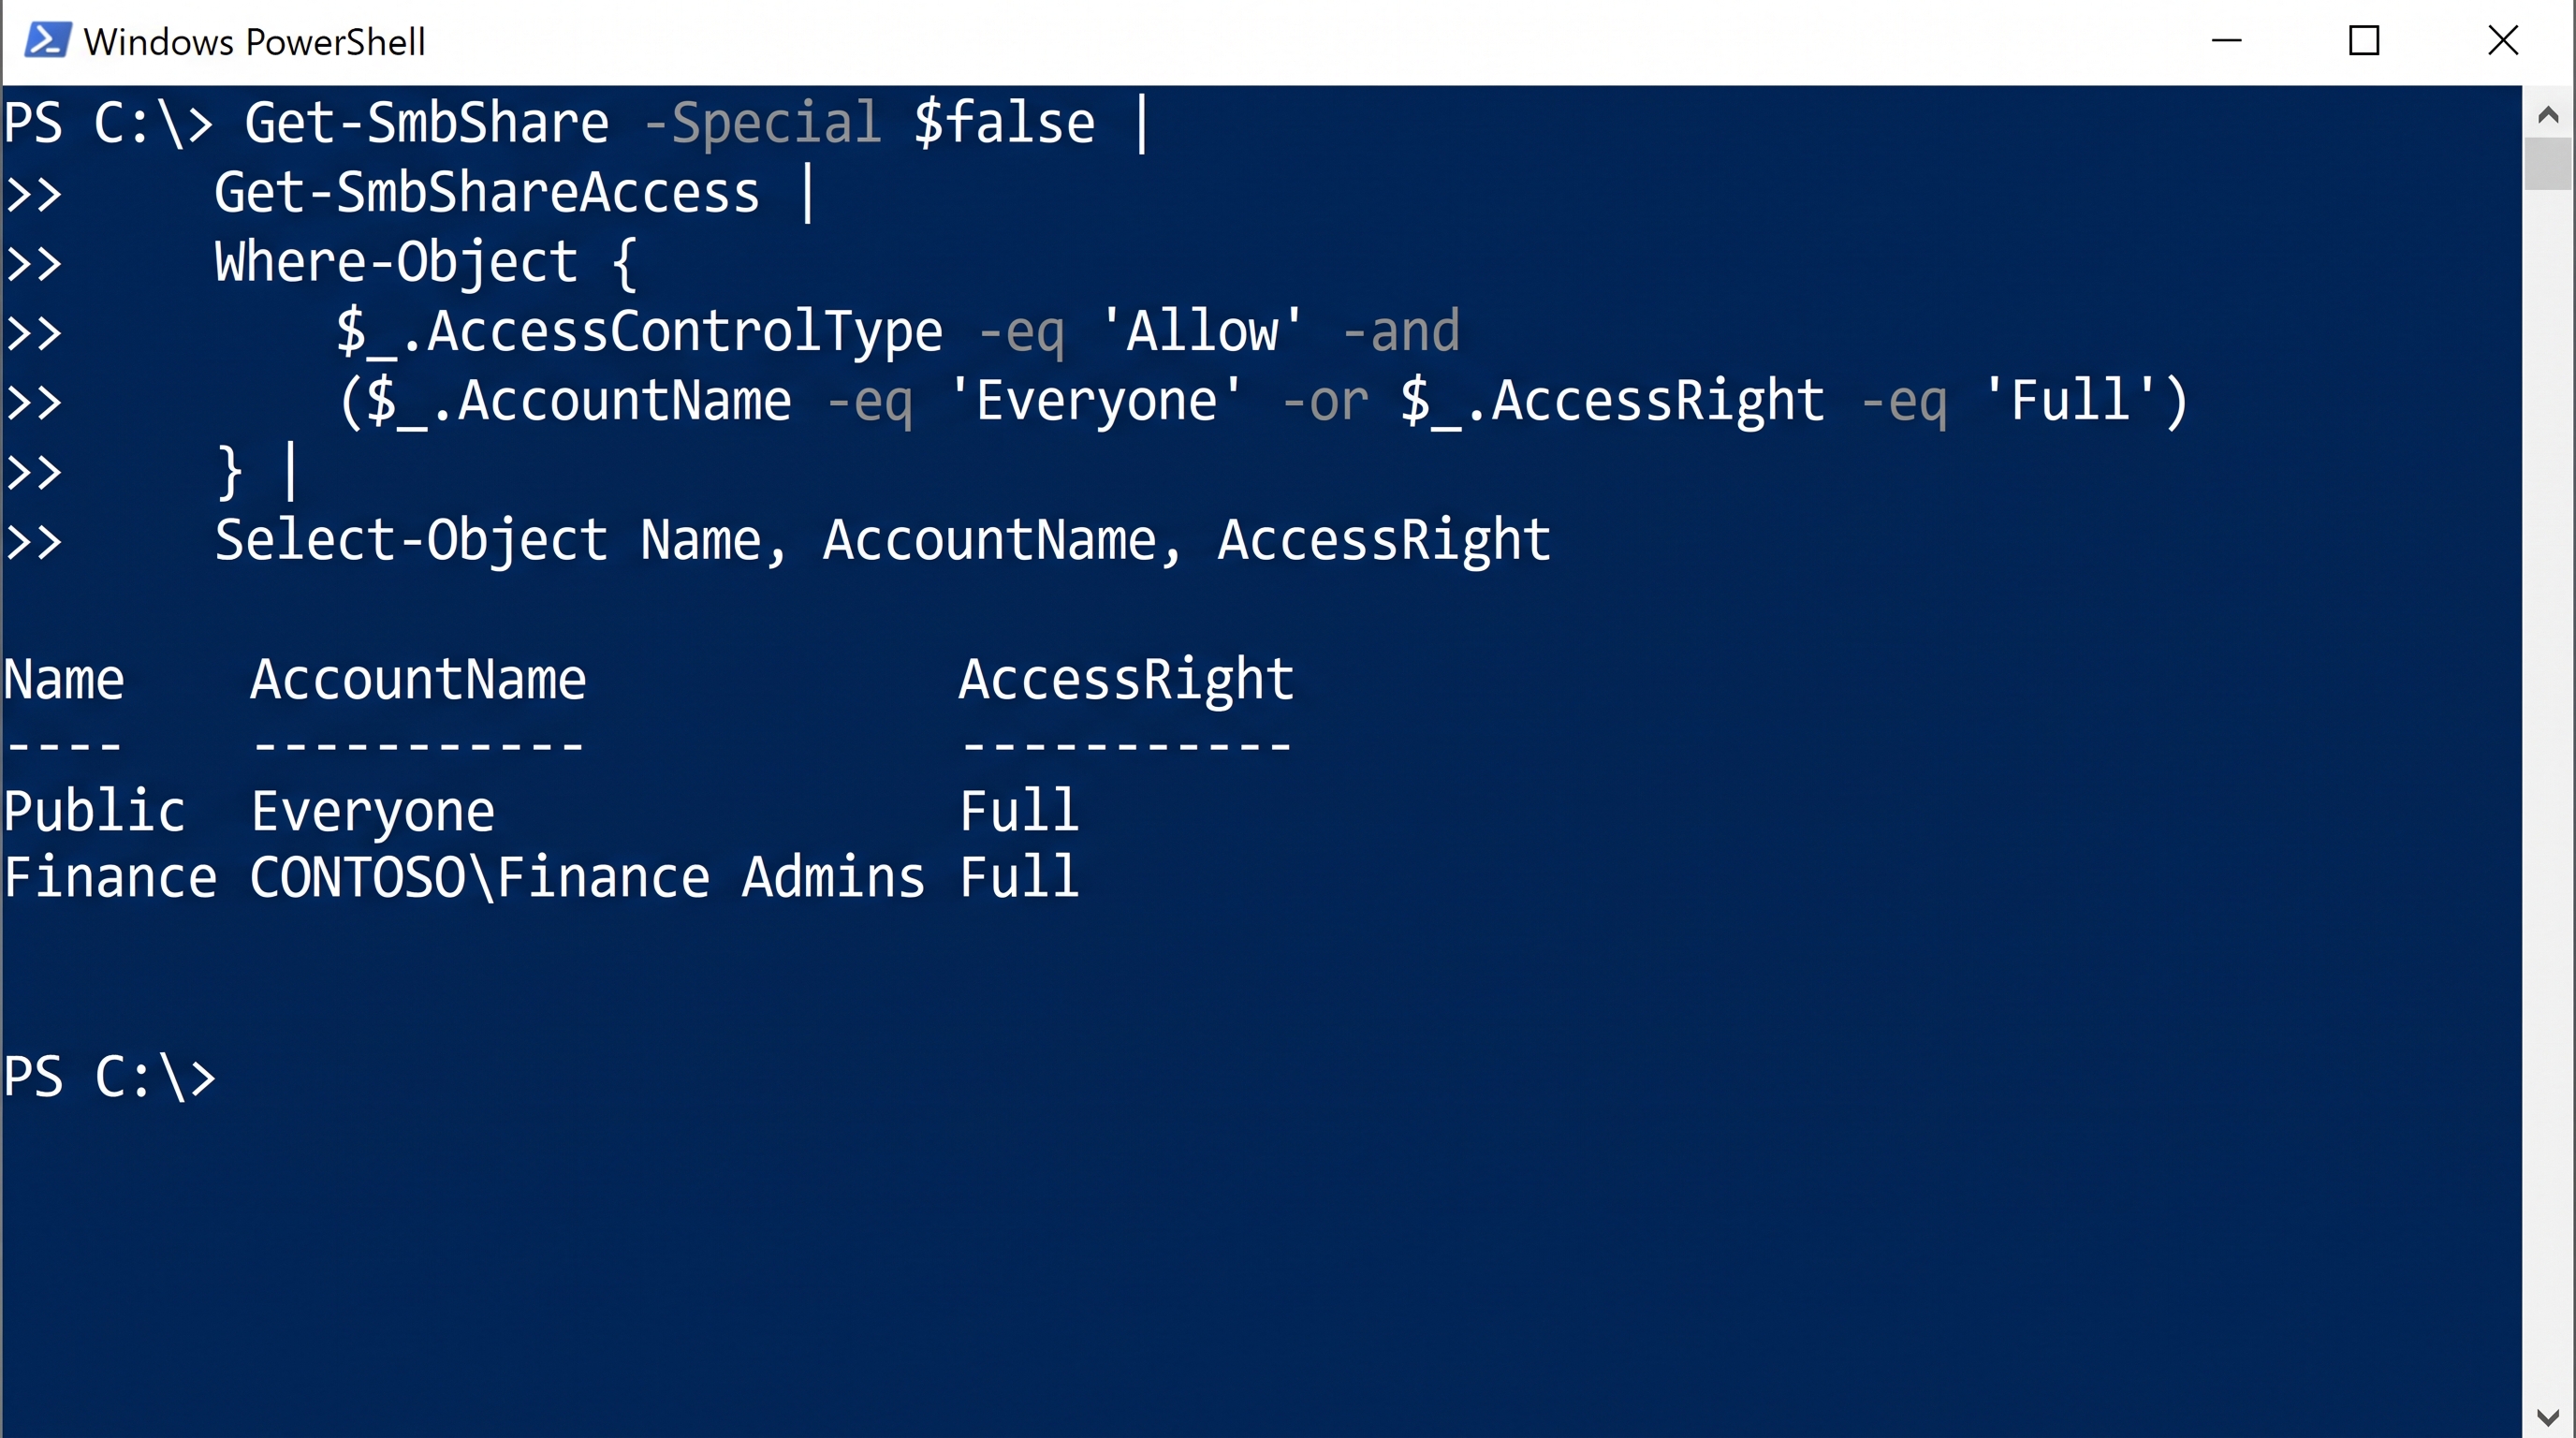
Every hit prints as one row, because the screenshot under reveals.
What Every Stage Does
| Stage | What It Does |
|---|---|
Get-SmbShare -Particular $false |
Drops admin and default shares. Microsoft’s -Particular parameter description names “Admin share, default shares, IPC$ share” as particular, so C$, ADMIN$ and IPC$ keep out. |
Get-SmbShareAccess |
“Retrieves the ACL of the SMB share.” Its -InputObject parameter accepts the share objects from the pipeline, so every share flows in with out a loop. |
The place-Object |
Retains Enable entries solely, as a result of a Deny entry for Everybody would in any other case print as a grant. Then retains Everybody, or any account with the Full proper. |
Choose-Object |
Trims the output to a few columns. |
CONTOSOFinance Admins reveals up too, as a result of the filter flags each Full grant, your individual admin teams included.
Warning: AccountName is a localized show title. On a non-English Home windows set up, Everybody prints below one other title, and the filter returns an empty desk. Run Get-SmbShareAccess as soon as unfiltered to see how your server prints it.
Audit Extra Than One Server
Open one session per server with New-CimSession and cross it to Get-SmbShare and Get-SmbShareAccess, since each settle for -CimSession. Every name then targets the server that owns the share:
$flag = {
    $_.AccessControlType -eq 'Enable' -and
    ($_.AccountName -eq 'Everybody' -or $_.AccessRight -eq 'Full')
}
foreach ($laptop in 'FS01', 'FS02')
        Get-SmbShareAccess -CimSession $session
New-CimSession connects over WinRM (port 5985 by default), so a server with out a listener errors out as an alternative of reporting clear.
Triage the Hits Earlier than Revoking Entry
Resist the urge to revoke on sight. The script reads solely the share ACL, so every row wants a learn of the NTFS ACL behind it:
| Script reveals | Which means | Subsequent verify |
|---|---|---|
| Everybody, Full | Share ACL totally open | Learn the NTFS ACL |
| Everybody, Learn or Change | Broad viewers, capped rights | Affirm the viewers |
| Named group, Full | Slender viewers, broad proper | Affirm membership |
| Nothing for an anticipated share | Clear, or a filter hole | Recheck the warning above |
One hole stays within the audit filter: an Authenticated Customers grant with Change or Learn matches neither take a look at, so it by no means prints. Run Get-SmbShareAccess unfiltered on any share whose viewers you doubt. To learn the NTFS facet, cross the share’s folder path to Get-Acl:
(Get-Acl -Path (Get-SmbShare -Title Public).Path).Entry |
    Choose-Object IdentityReference, FileSystemRights, AccessControlType
Get-Acl returns the safety descriptor for a file, folder, or registry key. If the NTFS ACL lists named teams, Everybody on the share is then precisely the setup Microsoft recommends. If it lists Everybody or Customers with Modify or FullControl, you’ve discovered actual publicity.
Take away the Grants You Can not Defend
For shares the place each ACLs are open, first grant the true viewers a named group with Grant-SmbShareAccess:
Grant-SmbShareAccess -Title 'Public' -AccountName 'CONTOSOPublic Customers' -AccessRight ChangeThen rehearse the elimination. Revoke-SmbShareAccess helps -WhatIf:
Revoke-SmbShareAccess -Title 'Public' -AccountName 'Everybody' -WhatIfWarning: Revoke-SmbShareAccess removes all enable entries for that account, and new connections that relied on Everybody lose entry once you affirm.
As soon as the preview appears proper:
-
Drop
-WhatIffrom the command and run it. -
Affirm the immediate.
-
Rerun the audit. The Public row ought to drop out of the outcomes. The Finance Admins row stays put.
Hold a listing of the Everybody grants you selected to go away, so the subsequent audit begins from recorded choices.

