The Microsoft Safe Boot certificates expires in 2026. Here’s a PowerShell script that retrieves the Safe Boot boot certificates info from all area computer systems and checks whether or not they comprise the CA 2023 certificates, and never older certificates.
Let’s dive in.
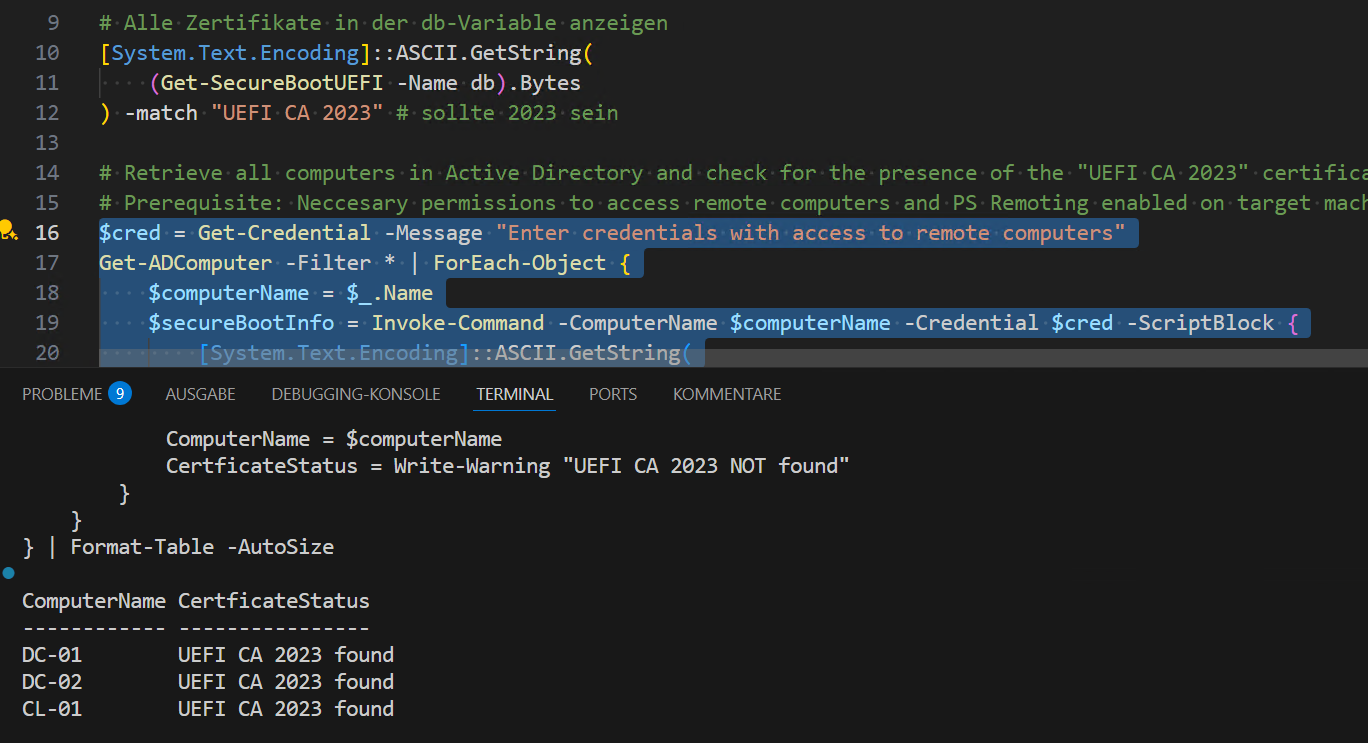
Run the next code on a website controller to retrieve details about the at the moment put in Safe Boot certificates in your distant computer systems. All techniques ought to report the CA 2023 certificates.
# Retrieve all computer systems in Energetic Listing and test for the presence of the "UEFI CA 2023" certificates
# Prerequisite: Neccesary permissions to entry distant computer systems and PS Remoting enabled on track machines (by way of GPO or Allow-PSRemoting)
$cred = Get-Credential -Message "Enter credentials with entry to distant computer systems"
Get-ADComputer -Filter * | ForEach-Object {
    $computerName = $_.Identify
    $secureBootInfo = Invoke-Command -ComputerName $computerName -Credential $cred -ScriptBlock {
        [System.Text.Encoding]::ASCII.GetString(
        (Get-SecureBootUEFI -Identify db).Bytes
        ) -match "UEFI CA 2023" # sollte 2023 sein
    }
    if ($secureBootInfo -eq $true) {
        [PSCustomObject]@{
            ComputerName = $computerName
            CertficateStatus = "UEFI CA 2023 discovered"
        }
    } else {
        [PSCustomObject]@{
            ComputerName = $computerName
            CertficateStatus = "UEFI CA 2023 NOT !!! discovered"
        }
    }
} | Format-Desk -AutoSize
See you subsequent time with PowerShell.
Revealed by Patrick Gruenauer
Microsoft MVP on PowerShell & Microsoft 365, IT-Coach, IT-Guide, MCSE: Cloud Platform and Infrastructure, Cisco Licensed Academy Teacher.
View all posts by Patrick Gruenauer