
In lots of organizations, managing Entra ID app registrations entails balancing the necessity for management with enterprise groups’ must combine functions shortly. Limiting the creation of app registrations to a small group of directors can shortly create bottlenecks. However, granting permissions too broadly can result in unmanaged functions with extreme entry.
This highlights a basic situation: the dearth of a structured course of for managing app registrations all through their lifecycle—in different phrases, end-to-end identification lifecycle administration.
What are app registrations in Entra ID?
An Entra ID app registration creates an identification for an utility within the tenant, corresponding to a consumer account for software program. The registration generates a novel Utility ID, an elective Listing Object ID, and the muse for authentication utilizing OAuth 2.0 or OpenID Join. The registration contains particulars corresponding to redirect URLs, permitted authentication strategies, and requested API permissions. As soon as the appliance receives admin consent, a service principal can also be created within the tenant—the article the appliance truly makes use of to function and request tokens.
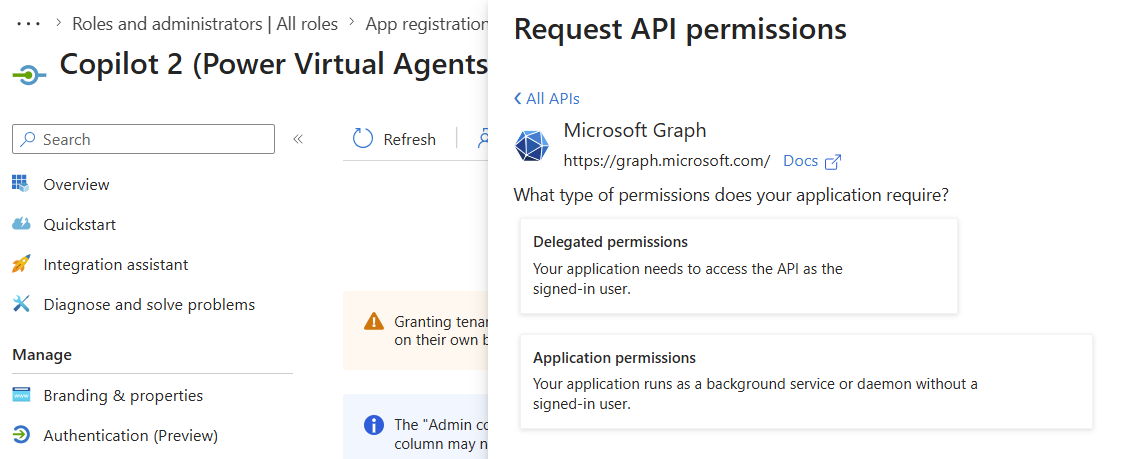
The excellence between delegated and utility permissions is especially vital. A delegated permission operates within the context of a signed-in consumer, whereas an utility permission can entry knowledge or sources independently of a consumer. If an utility permission with tenant-wide entry is unintentionally chosen for a restricted enterprise course of, a small integration venture can shortly turn into a far-reaching entry pathway.
Microsoft Graph is the central REST API behind Microsoft 365 and Entra ID, accessible at https://graph.microsoft.com. Whether or not studying customers, writing calendar entries, shifting SharePoint paperwork, or creating safety teams, these actions are typically carried out by calls to Microsoft Graph. The permissions an utility wants for Microsoft Graph endpoints are outlined utilizing delegated permissions or utility permissions. Scopes are permission parts that describe what an utility can do and have to be permitted by consent earlier than the primary manufacturing request.
Assessing the important permissions of app registrations
A scope corresponding to Mail.Learn can apply to the signed-in consumer’s mailbox. Mail.Learn.All, relying on the particular configuration, can enable entry to mailboxes throughout your entire tenant. Equally, Information.ReadWrite.All expands entry from particular person information to information in OneDrive and SharePoint. Permissions like these ought to due to this fact set off a further safety evaluation.
In apply, organizations ought to outline which scopes are permitted with out extra evaluation for every utility class, and which require approval from Safety or a tenant administrator. Permissions with the suffix .All deserve specific scrutiny as a result of they’ll considerably develop an utility’s potential attain.
Why doesn’t an admin-only method to app registrations scale?
Limiting app registrations to directors does present management, however in apply it doesn’t scale properly. Each new integration creates tickets, evaluation work, and ready occasions.
Directors turn into a bottleneck, SLAs come underneath stress, and enterprise groups lose momentum. This will result in workarounds corresponding to check tenants or unofficial integrations. Shadow IT is commonly not an try to interrupt the principles, however a symptom of lacking, scalable processes. With no structured lifecycle, an admin-only method leads both to delays or a lack of management—usually each.
Instance: An app registration for Controlling
For instance, a enterprise unit might have an utility that processes calendar knowledge for an inner capability evaluation. A structured portal captures the aim, proprietor, redirect URL, and required permissions. The request is reviewed from each a enterprise and safety perspective, then carried out routinely. After an outlined interval, the appliance is recertified. When the permitted utilization interval ends or the appliance is not wanted, its permissions and credentials could be revoked routinely, and the app could be decommissioned.
The app registration lifecycle in apply:
- Request: Seize the aim, proprietor, and required permissions
- Evaluate: Assess dangers and scope class
- Approval: Receive enterprise and technical approvals
- Implementation: Create the app, permissions, and credentials
- Operation: Monitor utilization, possession, and permissions
- Recertification: Verify the necessity for the app usually
- Decommissioning: Take away secrets and techniques, permissions, and the app
The important thing level is that creating an app registration shouldn’t be the top of the method. A managed lifecycle solely takes form when operation, common critiques, and an outlined decommissioning course of are included.
For extra details about app registrations and their technical administration, see the article Entra ID Integration for SSO and API Entry Management.
Limitations of Microsoft Entra ID for managing the app registration lifecycle
Microsoft Entra ID affords in depth options for creating and managing app registrations. Nonetheless, these primarily cowl the technical aspect, quite than the entire lifecycle of app registrations.
Key components of end-to-end identification lifecycle administration are sometimes lacking:
- No standardized request course of: App registrations are created immediately within the tenant, with no structured workflow or enterprise justification.
- No centralized permission governance: Which scopes are allowed is commonly left to the discretion of particular person directors.
- No lifecycle governance: As soon as created, app registrations stay in place with out computerized critiques or expiration mechanisms.
- No obligatory possession: App registrations usually don’t have any clearly assigned proprietor, particularly after an worker adjustments roles or leaves the group.
- Restricted built-in recertification: Common critiques have to be organized manually—or might not occur in any respect.
These limitations imply that app registrations may fit accurately from a technical perspective however should not embedded in a managed lifecycle.
That is the place a central platform is required to construction and govern the lifecycle at an organizational stage.
Sensible steps for directors
Organizations can take the next preliminary steps to higher management the app registration lifecycle, even with out a further platform:
Stock app registrations: Create an outline of present app registrations and their lively permissions.
Assign house owners: Each app registration ought to have a clearly assigned proprietor chargeable for its use and permissions.
Use delegated roles as a substitute of worldwide admin rights: Microsoft Entra ID allows you to delegate app administration rights utilizing restricted, customized roles, quite than granting registration rights solely to world directors throughout the board—or leaving them fully unrestricted. This enables chosen individuals or groups to handle particular app registrations with out giving them entry to different areas of Microsoft Entra.
Evaluate permissions usually: Utility permissions specifically must be reviewed at common intervals and diminished the place potential.
Limit admin consent intentionally: Important scopes shouldn’t be granted with out extra evaluation.
Set expiration dates for secrets and techniques: Quick-lived credentials cut back long-term safety dangers.
These measures can assist within the quick time period, however in bigger environments they shortly attain their limits as a result of they need to be carried out manually. That is the place structured identification lifecycle administration by automated IAM options—such because the FirstWare IDM-Portal from FirstAttribute AG—can add worth.
The IDM-Portal as a central management level
That is the place the FirstWare IDM-Portal is available in. The IAM answer helps identification lifecycle administration for functions, connecting organizational processes with technical implementation.
All requests are submitted by a central interface and processed utilizing outlined approval workflows. Implementation is automated, so candidates don’t want direct administrative permissions.
The lifecycle in apply (instance)
A enterprise consumer wants entry to an utility.
- Submit a request by the IDM-Portal
- Receive approval from the supervisor and, the place relevant, IT
- Routinely implement the change in Entra ID
Permissions are routinely reviewed after an outlined interval. Entry that’s not wanted is eliminated or adjusted.
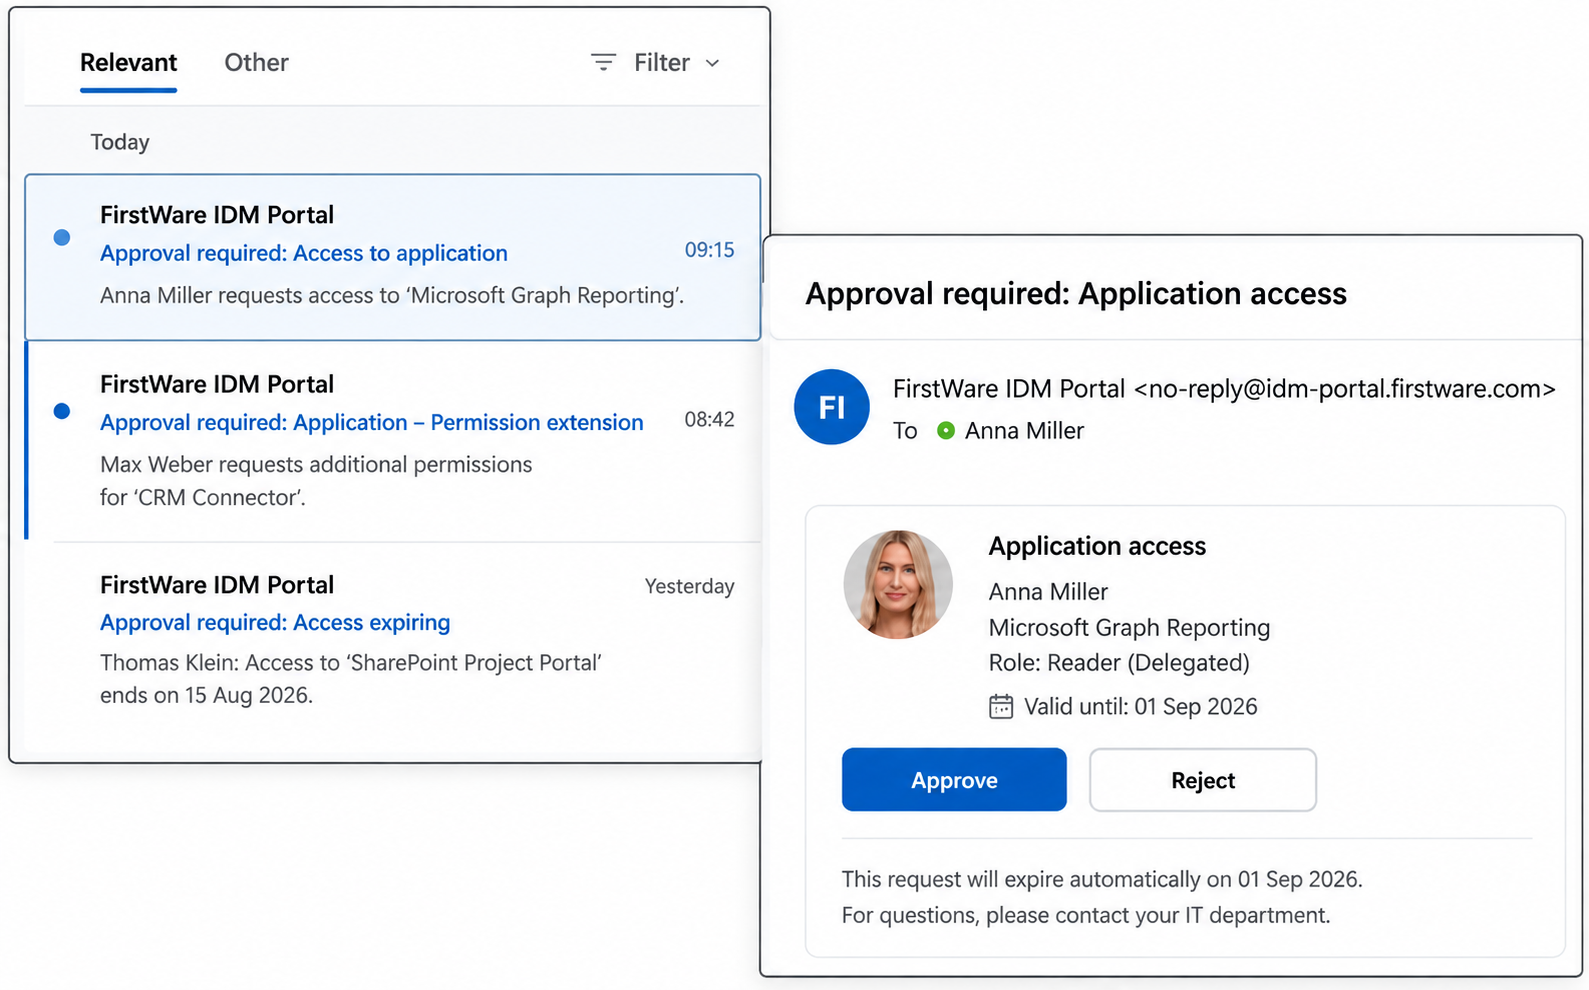
This creates a managed lifecycle as a substitute of permissions that stay lively indefinitely.
Advantages for organizations:
- CIO/CTO: Sooner implementation of latest integrations
- CISO: Lowered assault floor
- Compliance: Full traceability
Id lifecycle administration ensures that not solely entry is managed, however that entry rights are additionally saved updated over time.
Conclusion
App registrations in Entra ID stay a important part of recent IT environments. The true situation shouldn’t be the technical implementation or the query of “admins or enterprise groups,” however the lack of identification lifecycle administration. With no structured lifecycle, organizations face both IT bottlenecks or uncontrolled entry pathways.
Organizations that use IAM options such because the FirstWare IDM-Portal can stability safety and effectivity whereas sustaining management over their app registrations all through their complete lifecycle.
Did this provide help to? Share it or depart a remark:
Artikel erstellt am: 25.09.2026

