
TLDR: Multi-agent AI programs use specialised AI brokers to investigate repositories throughout structure, safety, efficiency, testing, and code high quality. By combining a number of views, they assist groups establish dangers earlier, prioritize enhancements, and tackle technical debt extra systematically.
Fashionable improvement groups ship options at an unbelievable tempo. AI coding assistants have accelerated improvement even additional, making it potential to generate massive quantities of code in minutes.
However as repositories develop, writing code is not the toughest half. Sustaining high quality throughout hundreds of recordsdata, a number of companies, and dozens of contributors turns into more and more tough.
Most groups nonetheless depend on:
- Handbook code critiques,
- Static evaluation instruments,
- Safety scans,
- Periodic structure critiques, and
- Technical debt audits.
These practices are precious, however they typically function as separate checks moderately than offering a unified view of repository well being.
A efficiency bottleneck may stay unnoticed till customers complain.
- Architectural points could solely floor when new options grow to be tough to implement.
- Safety vulnerabilities can go undetected till a lot later within the improvement cycle.
What groups want isn’t simply sooner code technology. They want a greater solution to perceive repository well being and prioritize enhancements.
That is the place multi-agent AI programs could make a significant distinction.
What’s a multi-agent AI system?
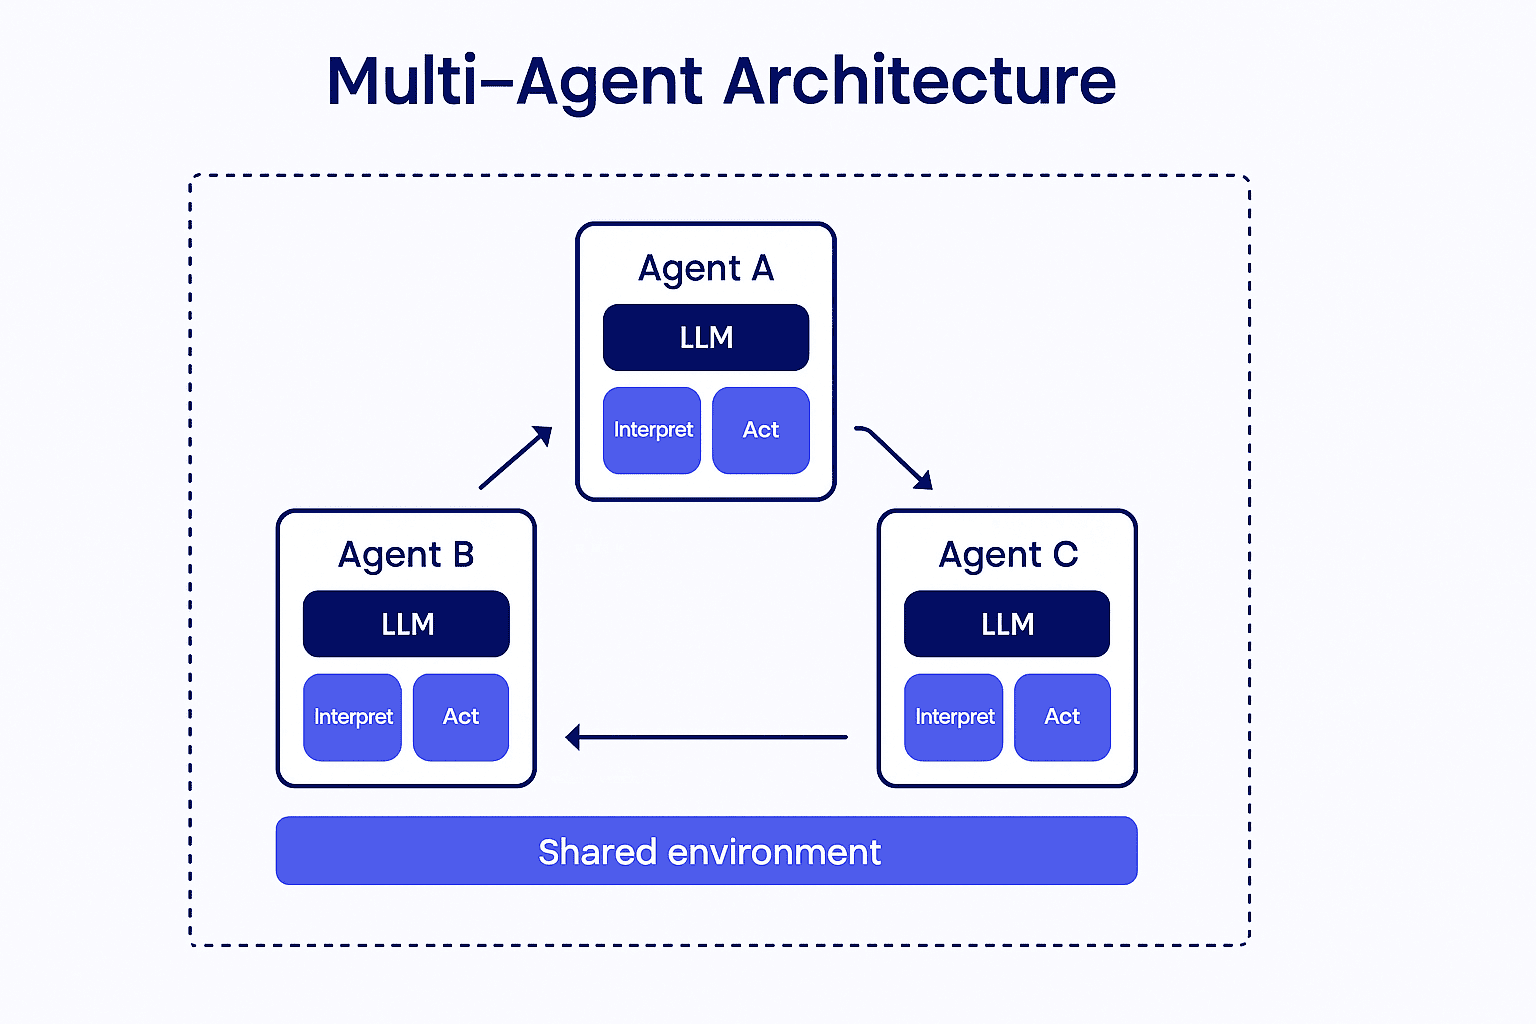
A multi-agent AI system makes use of a number of specialised AI brokers that collaborate to investigate and enhance a repository. As an alternative of asking one AI assistant to examine all the things, duties are divided amongst specialised reviewers.
Totally different brokers deal with areas resembling:
- Structure,
- Safety,
- Efficiency,
- Testing,
- Code high quality, and maintainability.
Collectively, they will present broader repository protection by analyzing completely different features of software program high quality concurrently. The precise worth will depend on how effectively the brokers are scoped, coordinated, and supported with related context.
A typical multi-agent system could:
- Analyze repository construction,
- Establish dangers and bottlenecks,
- Detect high quality points,
- Advocate enhancements,
- Prioritize findings, and
- Observe progress over time.
This transforms governance from an occasional evaluate exercise right into a extra systematic engineering course of.
When does a multi-agent method make sense?
Not each repository wants a multi-agent structure.
A multi-agent method typically is sensible when:
- The repository is massive or quickly rising.
- A number of high quality dimensions want analysis.
- Totally different groups personal completely different components of the system.
- Audits are carried out repeatedly.
- Findings should be consolidated and prioritized.
A single-agent method could also be higher when:
- The repository is comparatively small.
- Duties are narrowly scoped.
- Execution value is extra necessary than broad protection.
- There’s restricted cross-domain complexity.
The objective is to not substitute less complicated processes, however to introduce a number of specialised views when the repository’s complexity justifies it.
Why single-agent approaches can wrestle with complicated repositories
A single AI assistant behaves very like a succesful generalist developer. That method works effectively when reviewing a part, investigating a bug, or fixing a centered downside.
Fashionable functions, nevertheless, hardly ever include remoted issues.
For instance:
- A efficiency enchancment could introduce safety concerns.
- An architectural change can have an effect on testing protection.
- A deployment modification could impression reliability.
As complexity grows, groups typically profit from a number of specialised views.
When brokers are well-scoped and correctly coordinated, a multi-agent method can present broader protection, cut back blind spots, and make findings simpler to prepare.
The objective isn’t merely discovering extra points. It’s serving to groups establish the problems that matter most earlier than they grow to be costly issues.
Single-agent vs. Multi-agent approaches
| Side | Single-agent method | Multi-agent method |
| Duties | One agent handles a number of issues | Duties are divided amongst specialised brokers |
| Coordination | Easier | Requires orchestration |
| Area protection | Broad however doubtlessly shallow | Specialised throughout domains |
| Complexity | Decrease | Increased |
| Useful resource utilization | Often decrease | Will be increased |
| Failure dealing with | Fewer coordination factors | Extra coordination and failure factors |
| Greatest suited to | Centered duties | Advanced issues requiring a number of views |
Multi-agent programs are usually not mechanically higher. They introduce extra coordination, execution, and administration complexity. Their worth comes when specialization offers advantages that justify that added complexity.
Multi-agent architectures in follow
Multi-agent programs are generally applied utilizing both centralized or decentralized coordination.
| Structure | Greatest for | Commerce-off |
| Centralized | Constant coordination and shared decision-making | Dependency on central controller |
| Decentralized | Versatile agent-to-agent collaboration | Extra complicated coordination |
For repository governance eventualities, the selection will depend on whether or not consistency or flexibility is the upper precedence.
Specialised AI auditors for code governance
One of many greatest benefits of multi-agent AI programs is specialization. Relatively than asking one agent to guage all the things, completely different brokers deal with completely different features of software program high quality.
1. Structure auditor
Evaluates structural integrity, coupling, scalability issues, and repair boundaries.
Instance: Detects extreme dependencies between companies that make future modifications tougher.
2. Safety auditor
Identifies hardcoded secrets and techniques, authentication dangers, weak dependencies, and customary safety weaknesses.
Instance: Flags API keys dedicated immediately into supply management.
3. Efficiency auditor
Critiques question effectivity, useful resource utilization patterns, response time dangers, and optimization alternatives.
Instance: Identifies N+1 database question patterns that will improve latency.
4. Testing auditor
Evaluates check protection, edge-case dealing with, and testing gaps.
Instance: Detects fee processes with inadequate automated testing.
5. Code high quality and maintainability auditor
Identifies duplication, readability issues, documentation gaps, and maintainability points.
Instance: Highlights duplicate enterprise logic showing throughout a number of companies.
Collectively, these auditors assist groups develop a extra holistic understanding of repository well being.
Actual-world instance: Auditing a big SaaS repository
Contemplate a SaaS platform with:
- A number of microservices,
- Tons of of month-to-month pull requests,
- A number of engineering groups, and
- Rising technical debt.
The workforce lately adopted AI-assisted improvement and considerably elevated supply velocity. Nevertheless, repository well being turned tougher to grasp.
Pattern prioritized findings
| Discovering | Auditor | Precedence |
| Uncovered credentials in configuration | Safety | Essential |
| Lacking check protection in fee course of | Testing | Excessive |
| Costly database question affecting API response time | Efficiency | Excessive |
| Growing service coupling | Structure | Medium |
Individually, these findings are helpful. Collectively, they reveal broader dangers that may in any other case be missed.
As an alternative of receiving disconnected warnings, the engineering workforce receives a consolidated, prioritized view of repository well being.
That is the place multi-agent programs present significant worth: serving to groups transfer from remoted observations to knowledgeable engineering selections.
From findings to motion
Evaluation alone doesn’t enhance software program high quality. Groups should nonetheless determine what to repair first and the way to implement modifications.
Refactoring and planning
A planning part can:
- Consolidate findings,
- Take away duplicate suggestions,
- Prioritize points,
- Consider impression versus effort, and
- Present implementation steering.
Implementation help
Implementation-focused brokers could:
- Counsel refactorings,
- Generate code suggestions,
- Observe remediation progress, and
- Help with follow-up work.
Nevertheless, implementation ought to stay topic to developer evaluate and approval, significantly for security-sensitive, architectural, or production-impacting modifications.
The function of those programs is to assist groups uncover and set up enhancements, not substitute engineering judgment.
Operating your first multi-agent audit in Code Studio
Getting began with multi-agent governance in Syncfusion Code Studio is easy. The concept is straightforward: create a set of specialised AI auditors, level them at your repository, and allow them to analyze completely different features of code high quality in parallel.
Step 1: Create your AI brokers
Begin by creating the brokers you need to use within the .codestudio/brokers/ listing.
Choose the Configure Customized Brokers possibility within the chat interface. Create as many brokers as required.
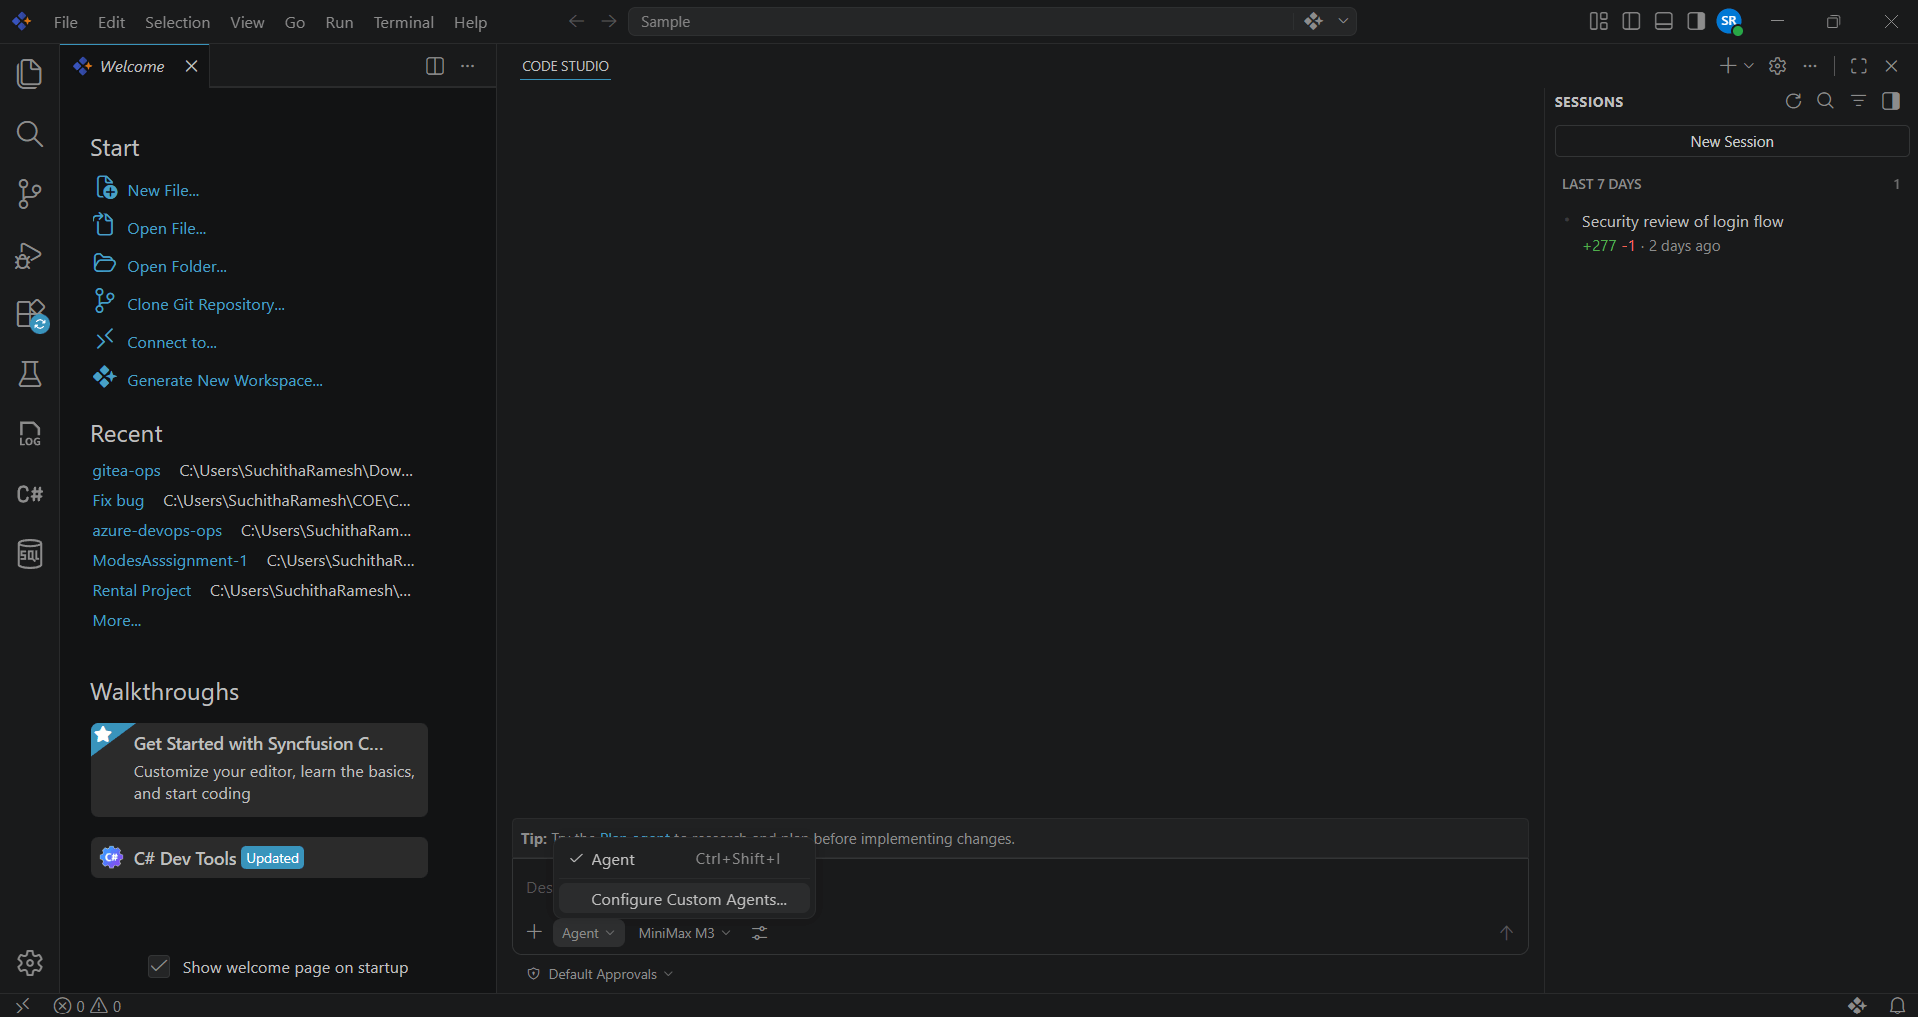
Widespread examples embody:
- Safety auditor,
- Structure auditor,
- Efficiency auditor,
- Testing auditor, and
- Code high quality auditor.
Every agent is outlined utilizing a easy Markdown configuration that describes its function and duties.
Multi-agent AI programs permit every auditor to deal with a selected space, leading to extra complete and actionable insights than a single general-purpose reviewer.
Step 2: Open your repository in Code Studio
As soon as your AI auditors are configured, open the repository you need to analyze in Code Studio and confirm that your .codestudio/brokers/ listing incorporates the brokers you’ve created.
A typical construction may appear to be:
| .codestudio/ └─ brokers/ ├─ security-auditor.md ├─ architecture-auditor.md ├─ performance-auditor.md └─ testing-auditor.md |
This listing acts as the invention level to your audit configuration.
When an audit begins, Code Studio mechanically identifies the obtainable brokers and invokes them primarily based on their outlined duties. By organizing brokers this manner, you’ll be able to simply customise the evaluation for various repositories.
For instance, a security-focused venture may use extra safety auditors, whereas a big enterprise utility could embody brokers for structure, maintainability, and DevOps critiques.
Step 3: Run a repository-wide audit
Together with your brokers configured and repository prepared, it’s time to allow them to get to work.
Run the next immediate within the Code Studio chat window:
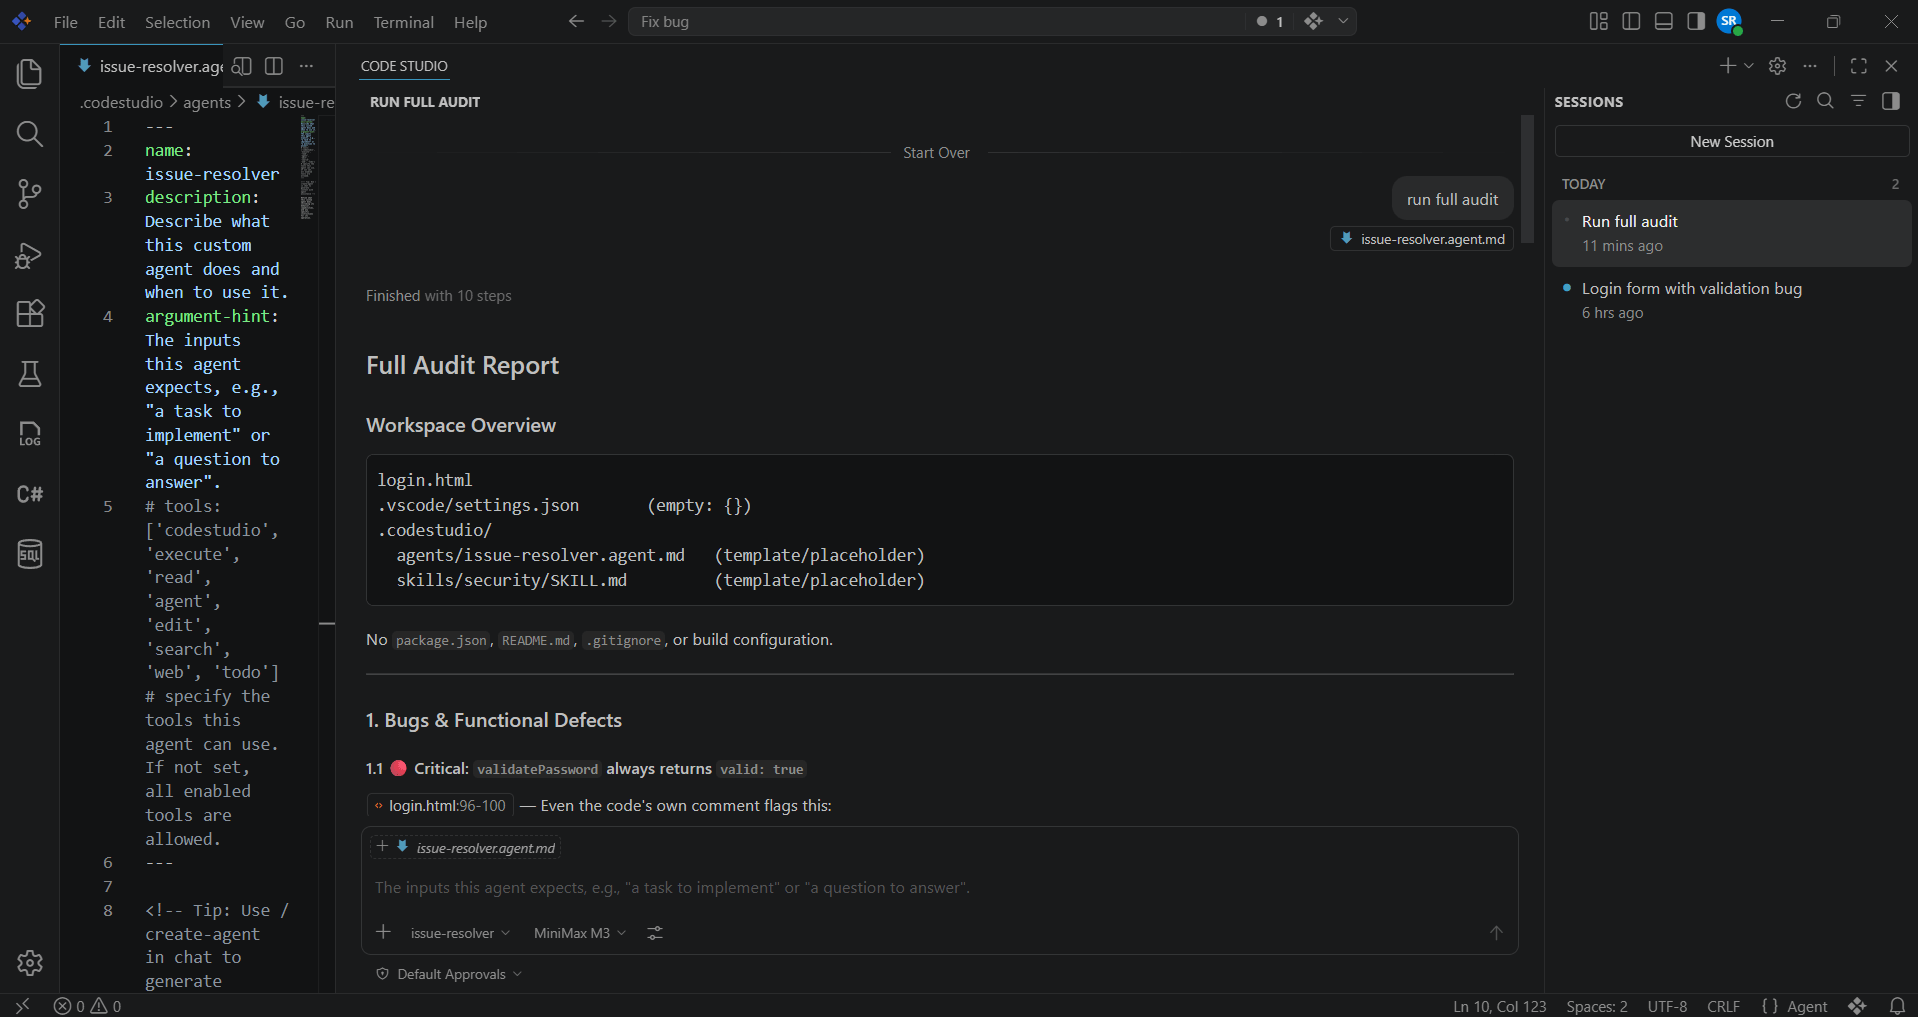
For bigger repositories, you’ll be able to velocity up the evaluation by working brokers in parallel:
Run full audit --parallelThis launches all configured auditors and begins analyzing your repository throughout a number of areas, together with structure, safety, efficiency, testing, maintainability, and code high quality.
Relatively than reviewing the codebase from a single perspective, every specialised agent focuses by itself area and stories findings independently. This enables groups to uncover a broader vary of points in a single audit run, from efficiency bottlenecks and safety dangers to architectural issues and testing gaps.
Step 4: Evaluate the generated stories
After the audit is accomplished, Code Studio organizes findings into structured stories that make it easier to transfer from subject discovery to motion.
You’ll usually discover stories resembling:
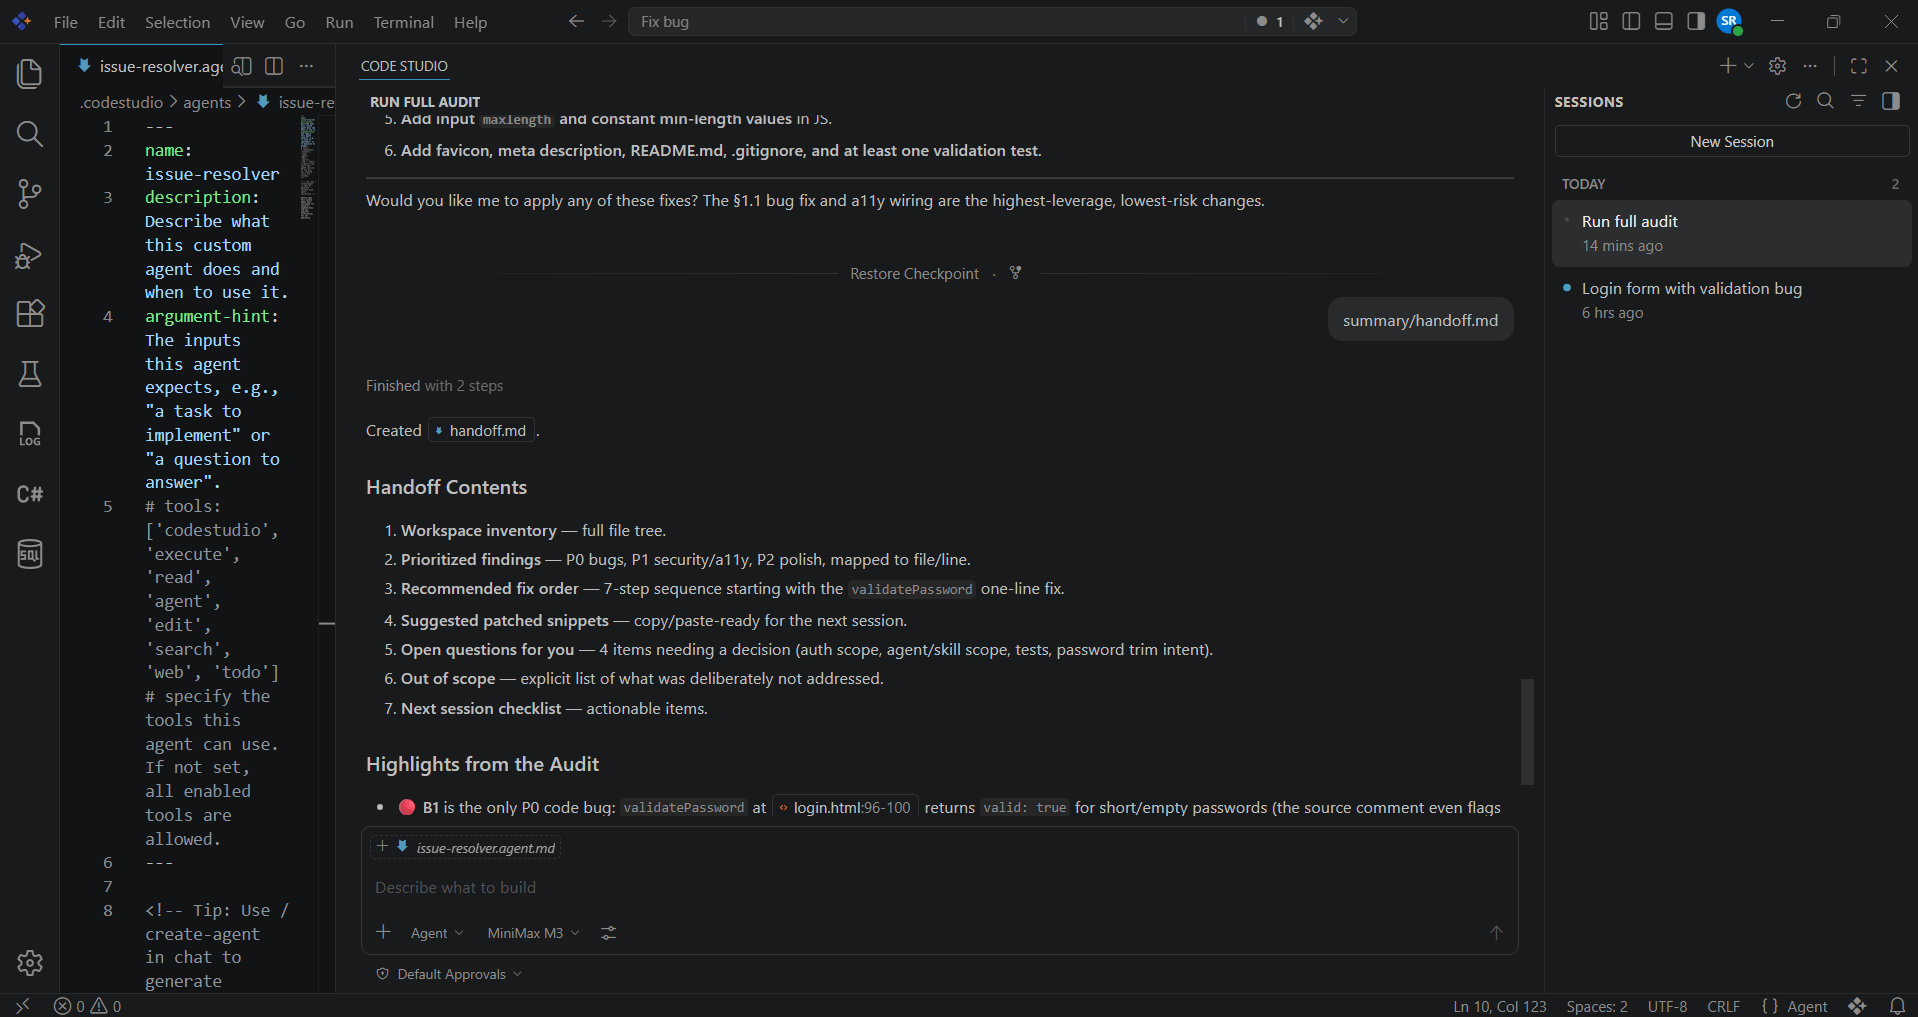
- abstract/handoff.md → General repository well being scorecard and key findings.
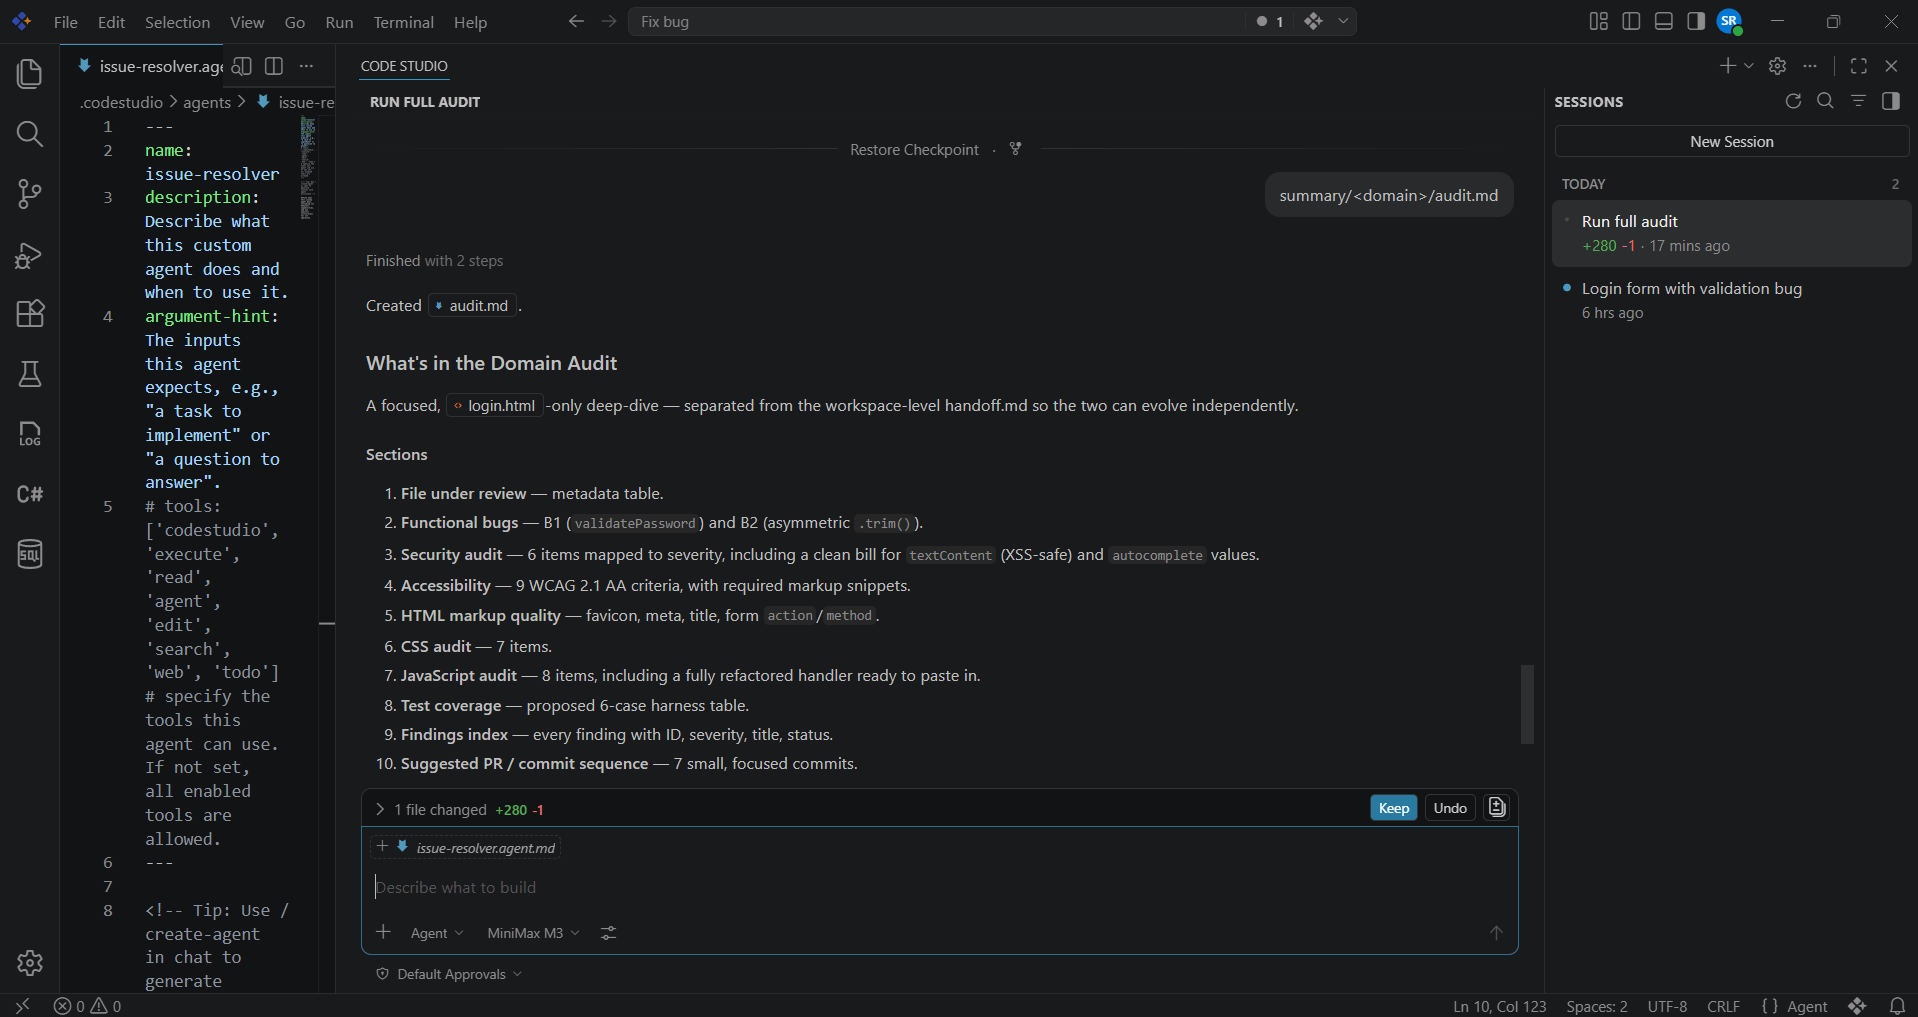
- abstract/<area>/audit.md → Detailed evaluation and recognized points.
- abstract/<area>/plan.md → Beneficial fixes and enchancment priorities.
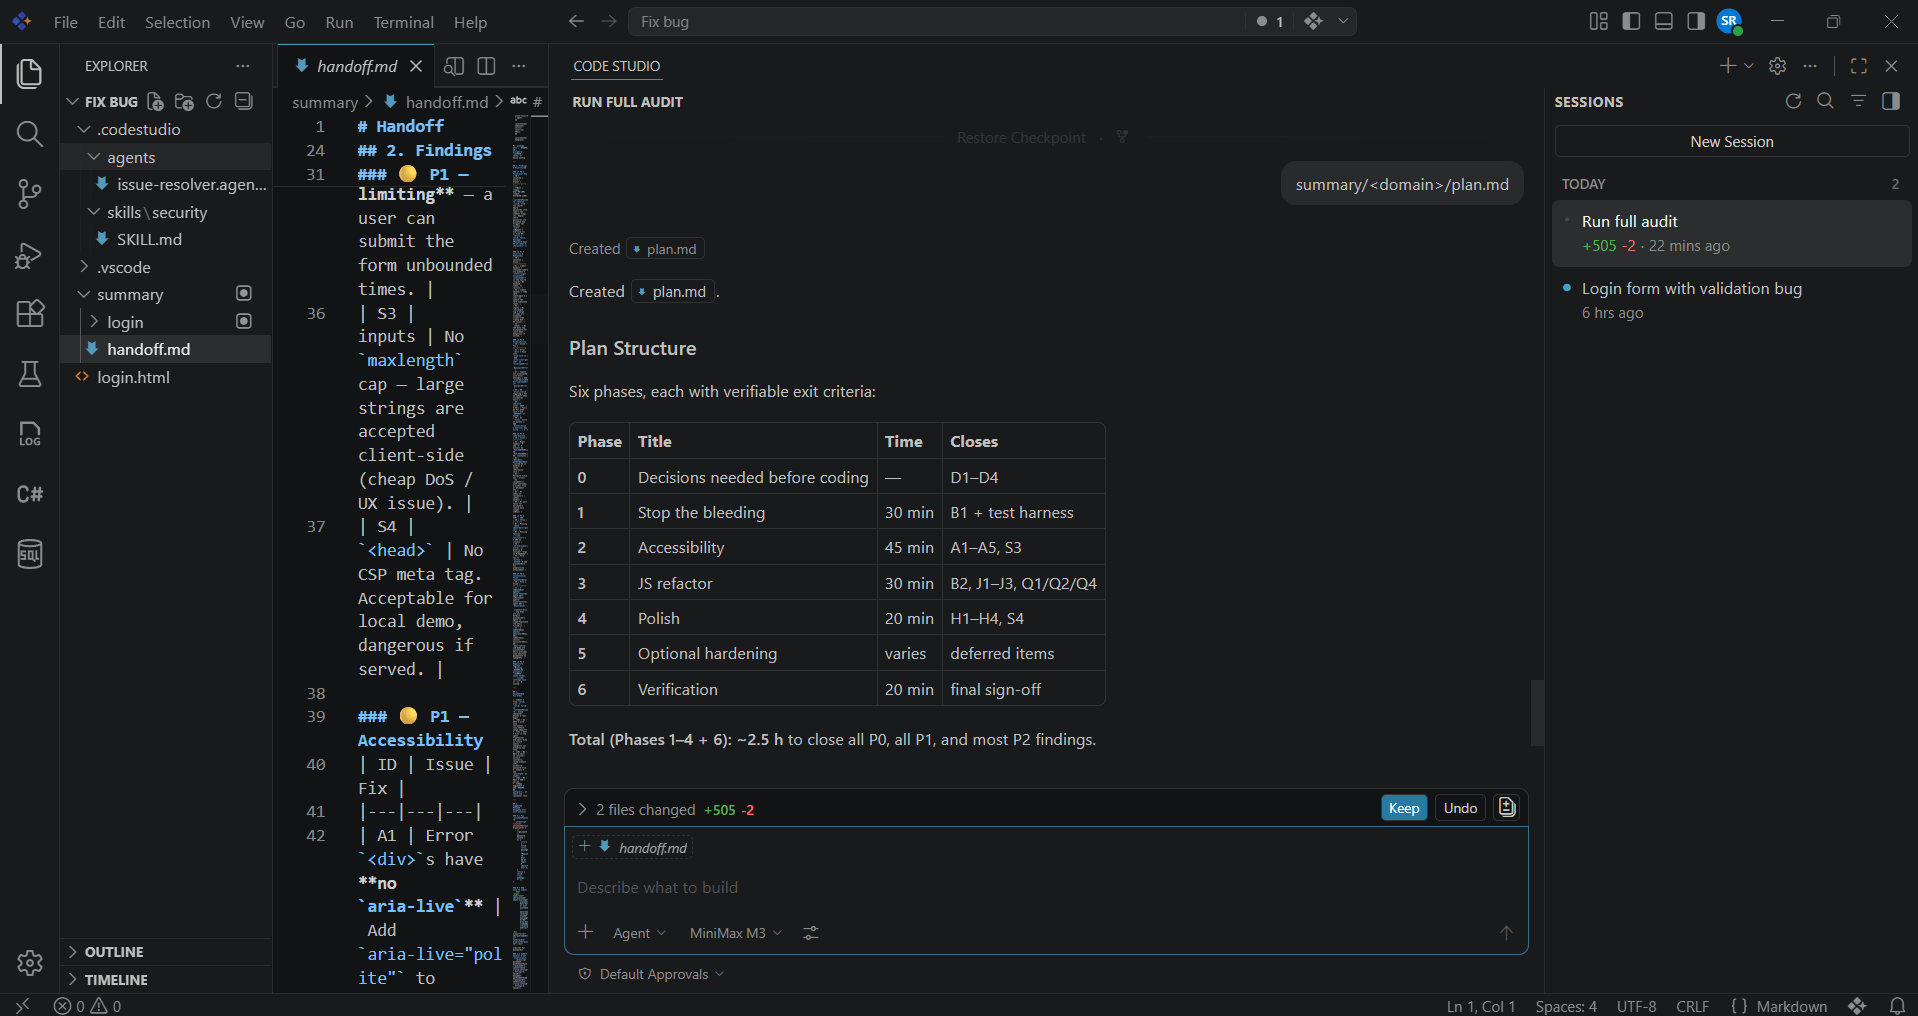
- abstract/<area>/progress.md → Implementation standing and monitoring.
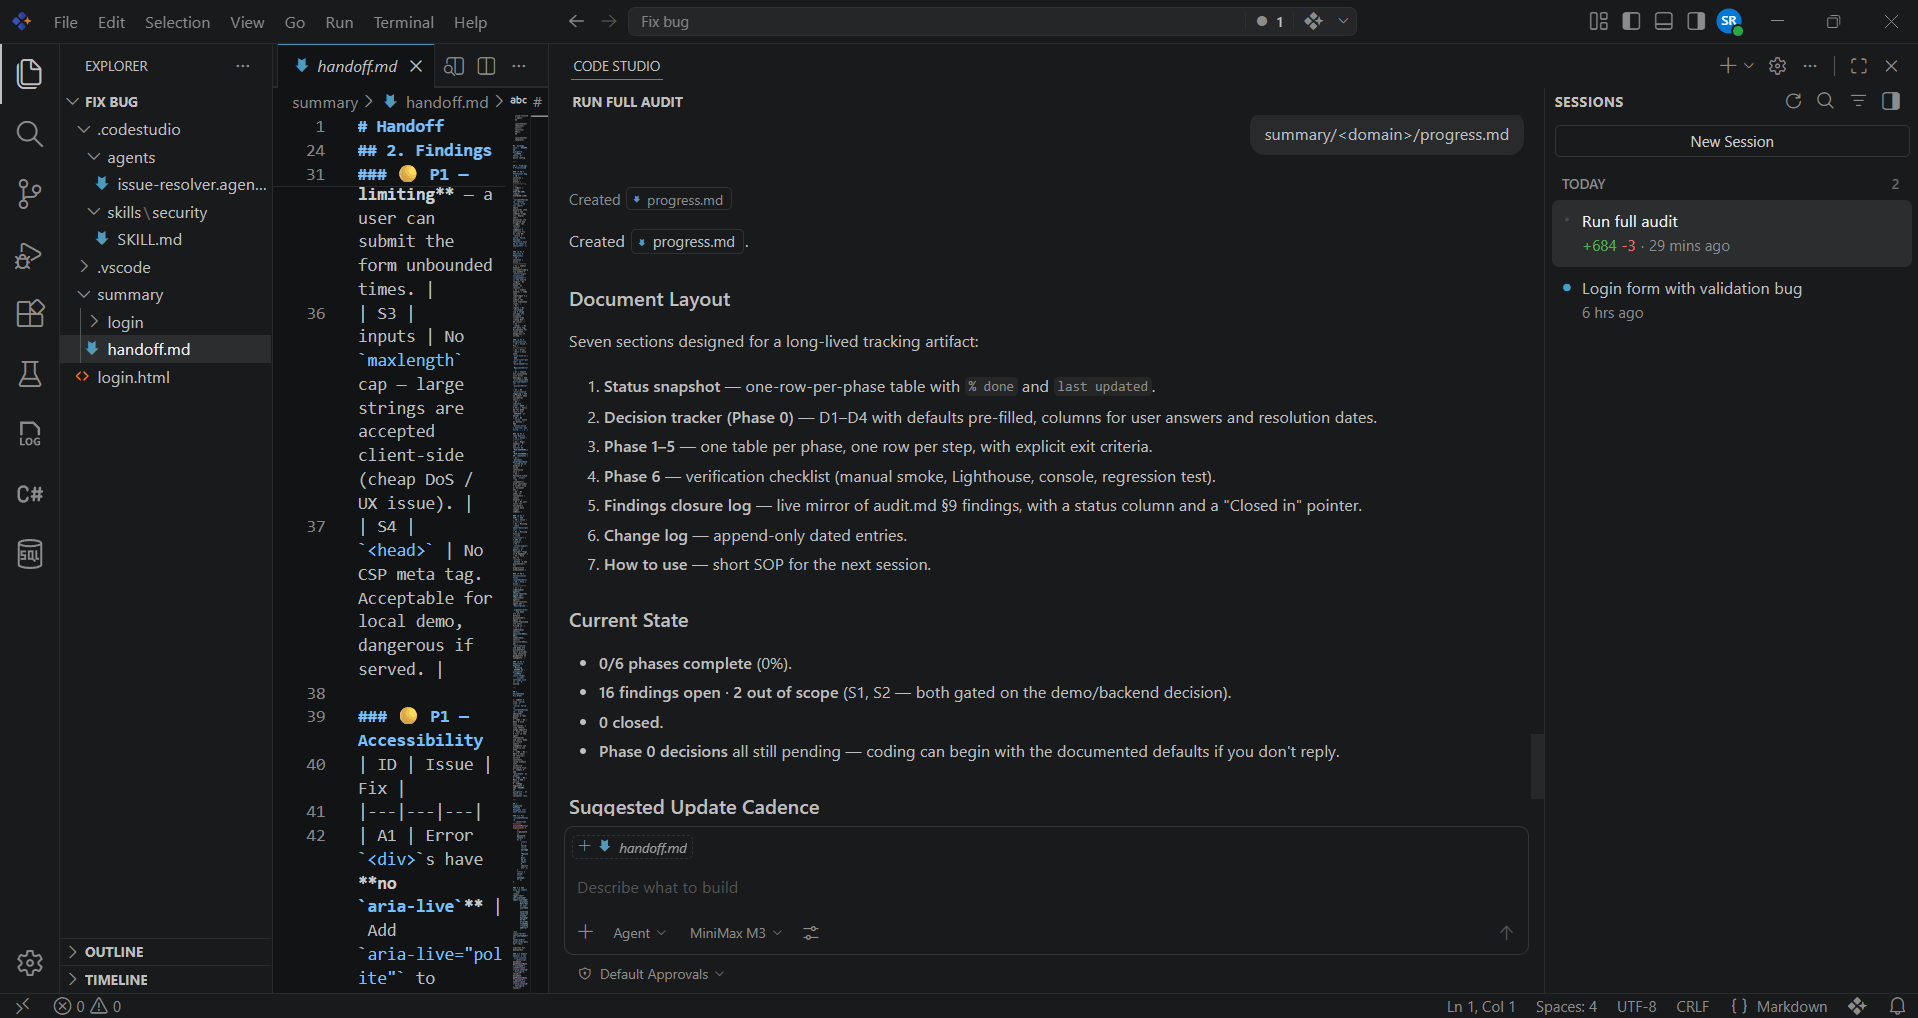
Relatively than presenting an extended record of remoted warnings, these stories present context round every discovering, together with the place it exists, why it issues, and what steps ought to be taken subsequent.
Step 5: Prioritize and implement enhancements
Discovering points is efficacious, however the actual impression comes from addressing the suitable ones first.
Use the generated plans to prioritize enhancements primarily based on danger, enterprise impression, and implementation effort. Widespread beginning factors embody:
- Fixing crucial safety vulnerabilities,
- Addressing architectural bottlenecks,
- Bettering check protection in high-risk areas, and
- Resolving efficiency and scalability issues.
A key benefit of multi-agent audits is that they assist groups deal with what issues most as an alternative of working by means of an extended, unstructured backlog. By highlighting the highest-impact points first, engineering groups could make measurable enhancements to repository well being whereas decreasing long-term technical debt.
With a prioritized plan in place, builders can transfer confidently from evaluation to implementation, making certain that enhancements are usually not solely recognized however systematically executed and tracked over time.
Manufacturing concerns
Multi-agent programs grow to be extra helpful when designed thoughtfully.
Vital concerns embody:
- Context-aware evaluation: Brokers ought to deal with areas related to the repository being analyzed.
- Duplicate discovering administration: Overlapping findings ought to be consolidated to cut back noise.
- Useful resource effectivity: Giant repositories can improve token utilization, execution value, and runtime necessities.
- Customization: Groups typically want the power to align audits with their very own engineering requirements and governance practices.
- Agent scope: Every agent ought to have a clearly outlined duty. Poorly scoped brokers typically produce overlapping or low-value findings.
- Shared context: Brokers want sufficient repository context to cause successfully with out unnecessarily duplicating info throughout a number of context home windows.
- Discovering construction: Findings are simpler to evaluate when brokers return a standard construction resembling:
-
- Severity,
- Location,
- Discovering,
- Proof,
- Influence, and
- Suggestion.
- Battle decision: Totally different brokers could often advocate conflicting actions. For instance:
- Confidence ranges: AI-generated findings ought to be handled as suggestions supported by proof moderately than as assured info.
These design decisions typically have a big impression on the usefulness of the ultimate output.
Conventional code evaluation vs. multi-agent AI code evaluate
| Conventional evaluation | Multi-agent AI audit |
| Rule-based checks | AI-driven reasoning |
| Predefined circumstances | Area-specific evaluation |
| Deterministic outcomes | Context-aware suggestions |
| Often centered on particular person points | Can join findings throughout domains |
| Decrease computational value | Probably increased execution value |
Multi-agent AI programs are usually not supposed to interchange static evaluation, safety scanners, checks, or human code evaluate.
As an alternative, they complement these instruments by including broader repository-level reasoning and prioritization.
The place multi-agent code audits ship worth
Multi-agent audits are significantly helpful for:
- Giant enterprise repositories,
- Multi-service and microservice functions,
- Groups adopting AI-assisted improvement,
- Safety-sensitive software program, and
- Organizations with a number of contributors and code house owners.
As complexity grows, specialised evaluation can grow to be more and more precious.
Limitations value understanding
Multi-agent AI programs are highly effective, however they don’t seem to be replacements for knowledgeable engineers.
Vital limitations embody:
- AI-generated findings could be incomplete or incorrect.
- A number of brokers could produce conflicting suggestions.
- Giant repositories can improve execution prices.
- Safety-sensitive modifications nonetheless require human validation.
- Enterprise and architectural selections stay human duties.
- A number of brokers can improve token utilization and execution prices.
- Broader repository evaluation could require extra context administration and orchestration.
- Extra brokers don’t mechanically end in higher outcomes.
The aim of those programs is to not get rid of builders from the method. Their worth lies in serving to builders spend much less time discovering issues and extra time fixing them.
Incessantly Requested Questions
What’s a multi-agent AI system?
A multi-agent AI system makes use of a number of specialised brokers that collaborate to investigate, monitor, or enhance a shared atmosphere.
How is it completely different from conventional code evaluate instruments?
Conventional instruments typically deal with particular checks in isolation.
Multi-agent programs mix a number of views and assist set up findings throughout completely different high quality domains.
Can multi-agent audits substitute human code critiques?
No. They work greatest as a complement to human critiques by figuring out dangers and alternatives earlier within the improvement course of.
Are multi-agent AI programs helpful for big repositories?
Sure. They are often significantly helpful for big repositories, supplied the system makes use of applicable scoping, context administration, orchestration, and useful resource controls.
What issues do multi-agent AI programs assist tackle?
They will help with technical debt, architectural drift, testing gaps, safety dangers, efficiency bottlenecks, and code high quality administration.
Take management of technical debt with Multi-agent AI programs
Producing code is turning into simpler on daily basis. Protecting code safe, maintainable, performant, and aligned with engineering requirements stays a rising problem.
Multi-agent AI programs assist tackle that problem by enabling specialised evaluation throughout structure, safety, efficiency, testing, and code high quality.
Relatively than relying solely on periodic critiques, groups can apply structured repository evaluation to establish dangers earlier and prioritize enhancements extra successfully.
As AI-assisted improvement accelerates, profitable groups will more and more mix sooner code technology with stronger code governance practices.
Syncfusion Code Studio permits groups to create specialised AI brokers, run repository-wide audits, and switch findings into actionable enchancment plans aligned with their engineering requirements.
The objective isn’t autonomous code governance. It’s giving engineering groups deeper visibility into repository well being and technical debt to allow them to make smarter selections at scale.
Able to see what your repository is absolutely telling you?
Begin your free trial or ebook a demo to discover AI-powered repository audits with Syncfusion Code Studio.

